Cheat
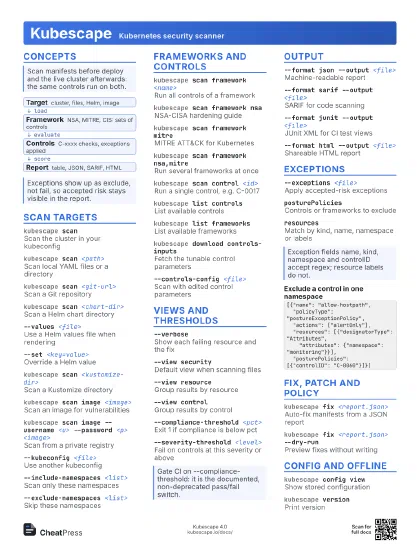
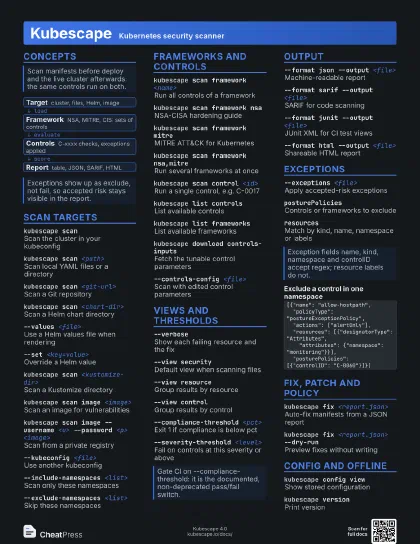
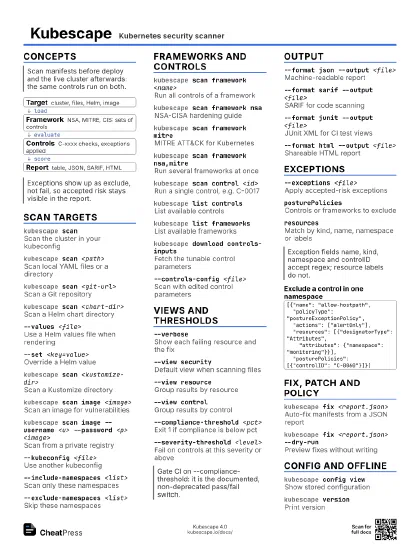
Kubescape Kubernetes security scanner
 Light · Postcard
102 × 152 mm · PDF
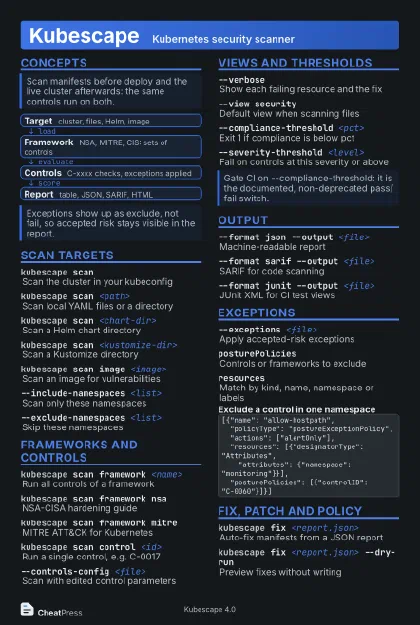 Dark · Postcard
102 × 152 mm · PDF
 Ink saver · Postcard
102 × 152 mm · PDF
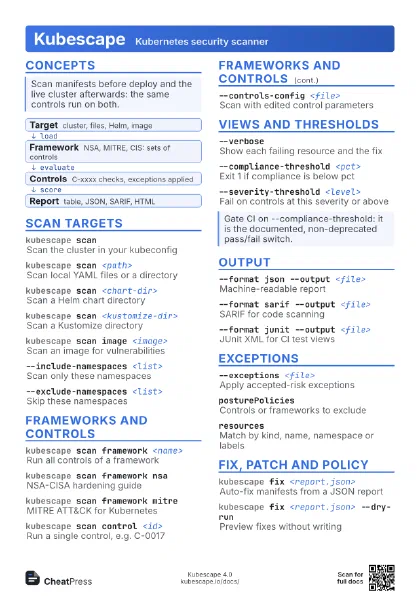
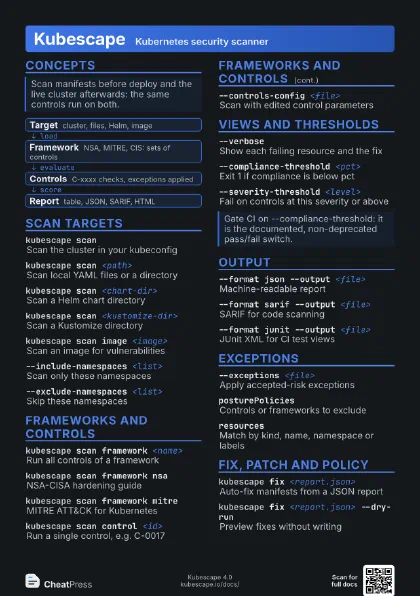
 Light · A4 landscape
297 × 210 mm · PDF
 Dark · A4 landscape
297 × 210 mm · PDF
 Ink saver · A4 landscape
297 × 210 mm · PDF
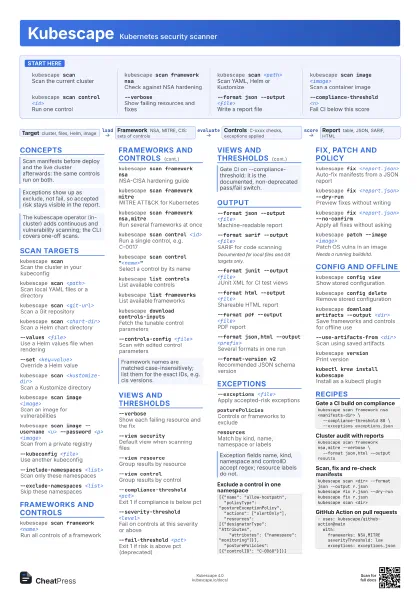
 Light · A3 landscape
420 × 297 mm · PDF
 Dark · A3 landscape
420 × 297 mm · PDF
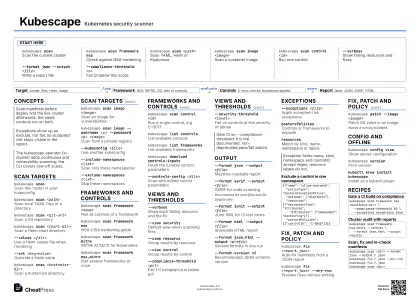 Ink saver · A3 landscape
420 × 297 mm · PDF
Start here
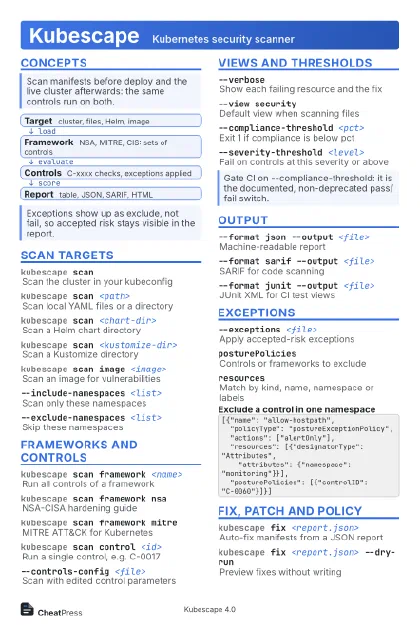
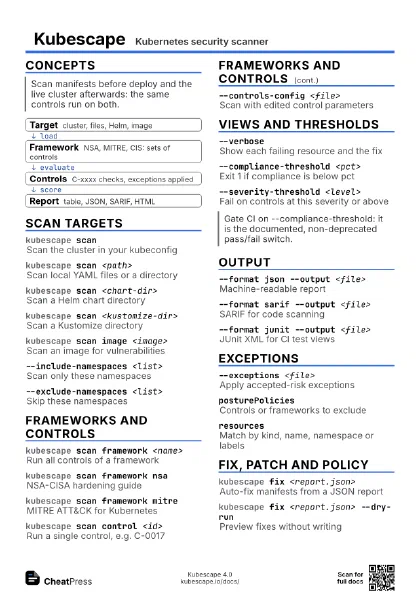
kubescape scanScan the current cluster
kubescape scan framework nsa
Check against NSA hardening
kubescape scan <path>
Scan YAML, Helm or Kustomize
kubescape scan image <image>
Scan a container image
kubescape scan control <id>
Run one control
--verboseShow failing resources and fixes
--format json --output <file>
Write a report file
--compliance-threshold <n>
Fail CI below this score
Concepts
- Target cluster, files, Helm, image
- Framework NSA, MITRE, CIS: sets of controls
- Controls C-xxxx checks, exceptions applied
- Report table, JSON, SARIF, HTML
Scan targets
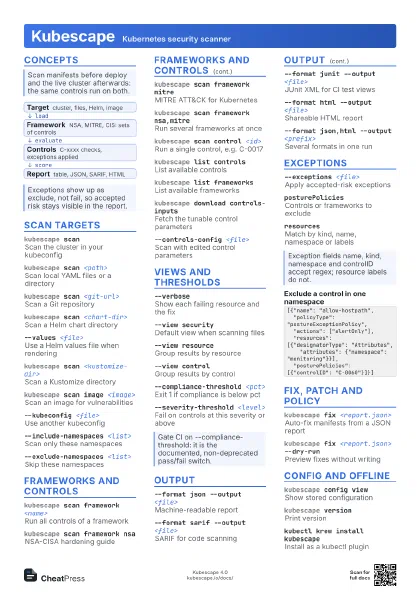
kubescape scanScan the cluster in your kubeconfig
kubescape scan <path>
Scan local YAML files or a directory
kubescape scan <git-url>
Scan a Git repository
kubescape scan <chart-dir>
Scan a Helm chart directory
--values <file>
Use a Helm values file when rendering
--set <key=value>
Override a Helm value
kubescape scan <kustomize-dir>
Scan a Kustomize directory
kubescape scan image <image>
Scan an image for vulnerabilities
kubescape scan image --username <u> --password
                    <p> <image>
Scan from a private registry
--kubeconfig <file>
Use another kubeconfig
--include-namespaces <list>
Scan only these namespaces
--exclude-namespaces <list>
Skip these namespaces
Frameworks and controls
kubescape scan framework <name>
Run all controls of a framework
kubescape scan framework nsa
NSA-CISA hardening guide
kubescape scan framework mitre
MITRE ATT&CK for Kubernetes
kubescape scan framework nsa,mitre
Run several frameworks at once
kubescape scan control <id>
Run a single control, e.g. C-0017
kubescape scan control "<name>"
Select a control by its name
kubescape list controls
List available controls
kubescape list frameworks
List available frameworks
kubescape download controls-inputs
Fetch the tunable control parameters
--controls-config <file>
Scan with edited control parameters
Views and thresholds
--verboseShow each failing resource and the fix
--view securityDefault view when scanning files
--view resourceGroup results by resource
--view controlGroup results by control
--compliance-threshold <pct>
Exit 1 if compliance is below pct
--severity-threshold <level>
Fail on controls at this severity or above
--fail-threshold <pct>
Exit 1 if risk is above pct (deprecated)
Output
--format json --output <file>
Machine-readable report
--format sarif --output <file>
SARIF for code scanning
Documented for local files and Git targets only.
--format junit --output <file>
JUnit XML for CI test views
--format html --output <file>
Shareable HTML report
--format pdf --output <file>
PDF report
--format markdown --output <file>
Markdown report
--format csv --output <file>
CSV report
--format json,html --output <prefix>
Several formats in one run
--format-version v2
Recommended JSON schema version
--hidePseudonymize sensitive metadata
--encrypt
Encrypt metadata with KUBESCAPE_MASTER_KEY
kubescape decrypt <report.json>
Decrypt an encrypted report
Exceptions
--exceptions <file>
Apply accepted-risk exceptions
posturePoliciesControls or frameworks to exclude
resourcesMatch by kind, name, namespace or labels
actions: ["alertOnly"]
The only supported exception action
[{"name": "allow-hostpath", "policyType": "postureExceptionPolicy", "actions": ["alertOnly"], "resources": [{"designatorType": "Attributes", "attributes": {"namespace": "monitoring"}}], "posturePolicies": [{"controlID": "C-0060"}]}]Fix, patch and policy
kubescape fix <report.json>
Auto-fix manifests from a JSON report
kubescape fix <report.json> --dry-run
Preview fixes without writing
kubescape fix <report.json> --no-confirm
Apply all fixes without asking
kubescape patch --image <image>
Patch OS vulns in an image
Needs a running buildkitd.
kubescape vap deploy-library
Print the ValidatingAdmissionPolicy library
kubescape vap create-policy-binding -n <name> -p
                    <control>
Bind a policy to namespaces
kubescape predict pss -n <namespace>
Predict Pod Security Standard level
kubescape operator scan configurations
Trigger a scan via the in-cluster operator
Config and offline
kubescape config view
Show stored configuration
kubescape config set <key> <value>
Set a config value
kubescape config delete
Remove stored configuration
kubescape download artifacts --output <dir>
Save frameworks and controls for offline use
--use-artifacts-from <dir>
Scan using saved artifacts
kubescape download framework <name> --output
                    <file>
Save one framework
--use-from <file>
Scan with a saved framework file
kubescape version
Print version
kubescape mcpserver
Start the MCP server
kubectl krew install kubescape
Install as a kubectl plugin
Recipes
kubescape scan framework nsa <manifests-dir> \ --compliance-threshold 80 \ --exceptions exceptions.jsonkubescape scan framework nsa,mitre --verbose \ --format json,html --output resultskubescape scan <dir> --format json --output r.jsonkubescape fix r.json --dry-runkubescape fix r.jsonkubescape scan <dir>- uses: kubescape/github-action@main with: frameworks: NSA,MITRE severityThreshold: low exceptions: exceptions.json