Cheat
socat Bidirectional byte relay
 Light · Postcard
102 × 152 mm · PDF
 Dark · Postcard
102 × 152 mm · PDF
 Ink saver · Postcard
102 × 152 mm · PDF
 Light · A4 landscape
297 × 210 mm · PDF
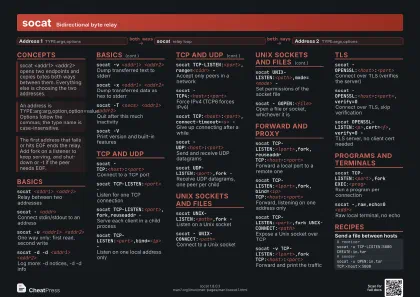 Dark · A4 landscape
297 × 210 mm · PDF
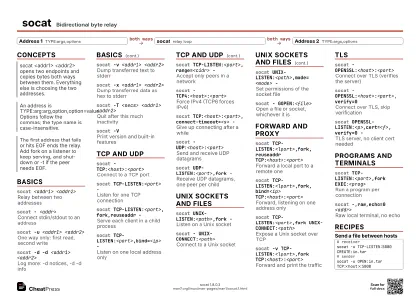 Ink saver · A4 landscape
297 × 210 mm · PDF
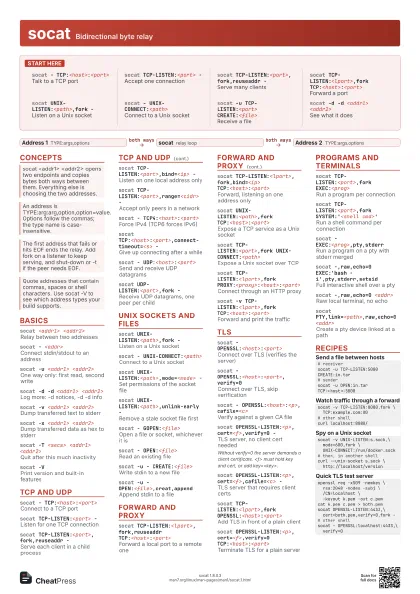
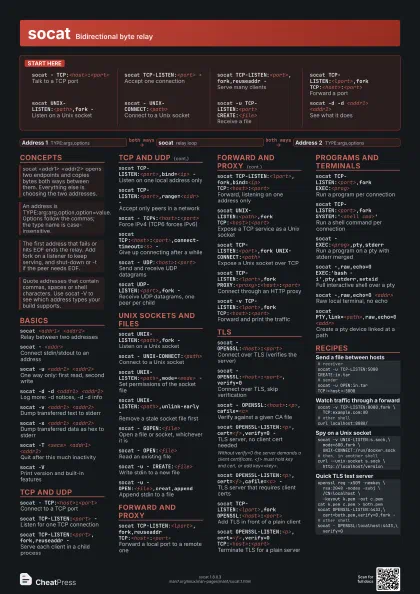
 Light · A3 landscape
420 × 297 mm · PDF
 Dark · A3 landscape
420 × 297 mm · PDF
 Ink saver · A3 landscape
420 × 297 mm · PDF
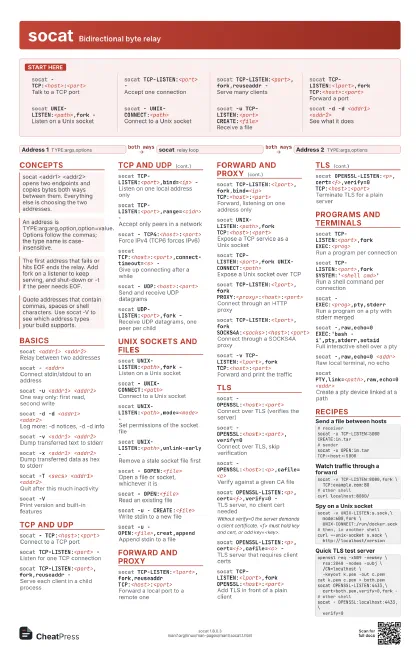
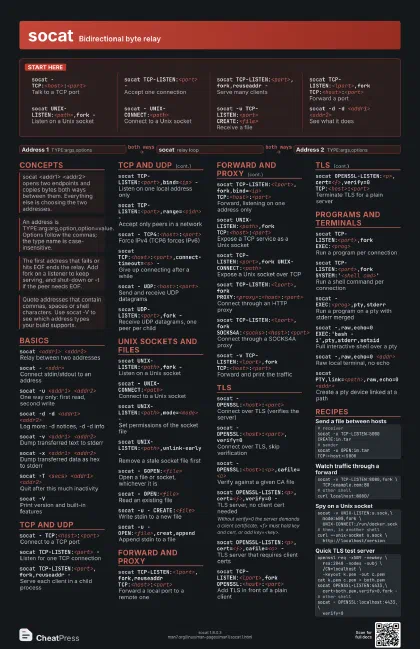
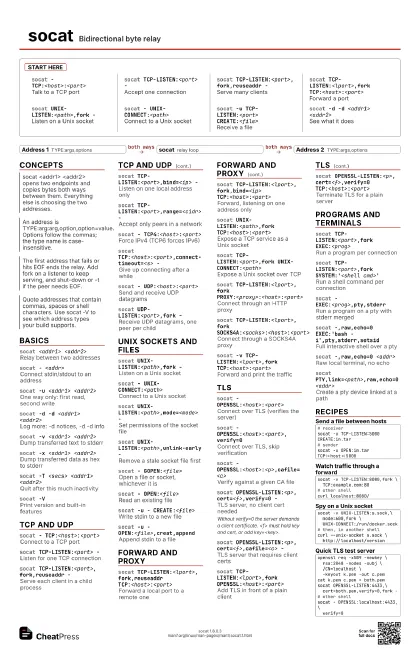
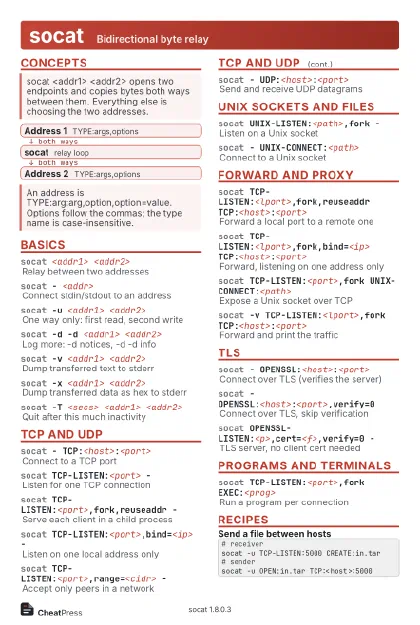
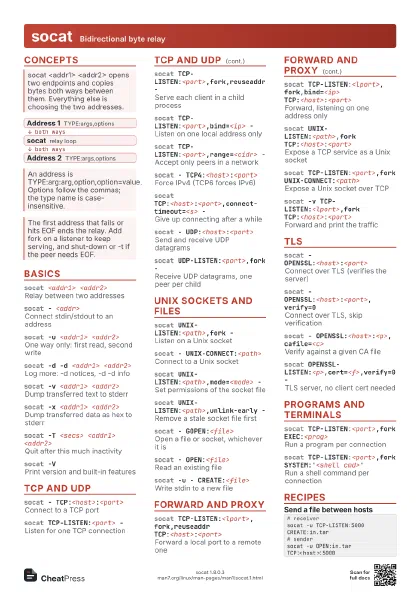
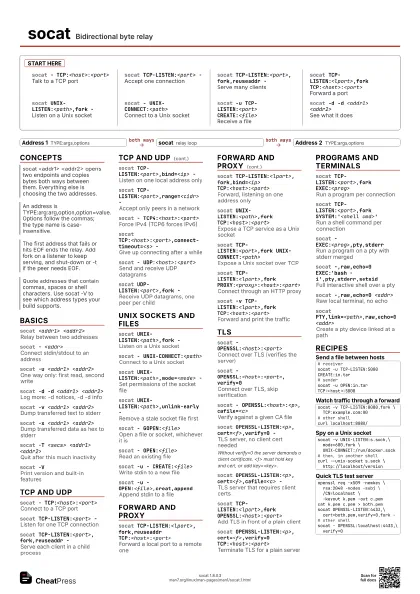
Start here
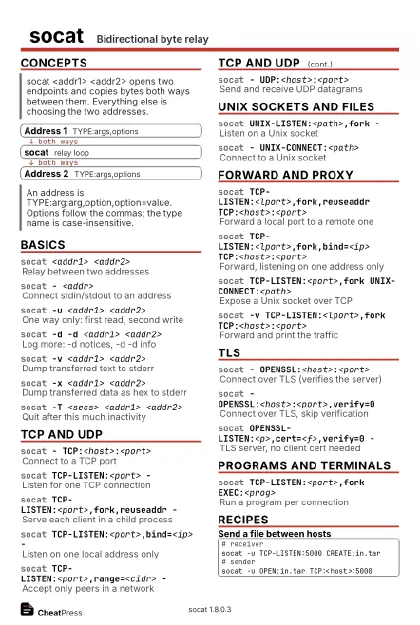
socat - TCP:<host>:<port>
Talk to a TCP port
socat TCP-LISTEN:<port> -
Accept one connection
socat TCP-LISTEN:<port>,fork,reuseaddr -
Serve many clients
socat TCP-LISTEN:<lport>,fork
                    TCP:<host>:<port>
Forward a port
socat UNIX-LISTEN:<path>,fork -
Listen on a Unix socket
socat - UNIX-CONNECT:<path>
Connect to a Unix socket
socat -u TCP-LISTEN:<port> CREATE:<file>
Receive a file
socat -d -d <addr1> <addr2>
See what it does
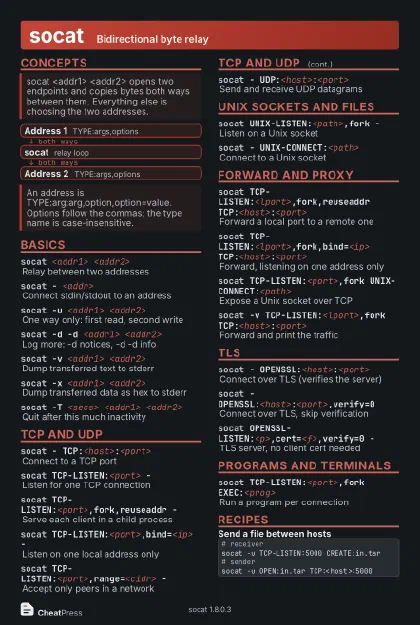
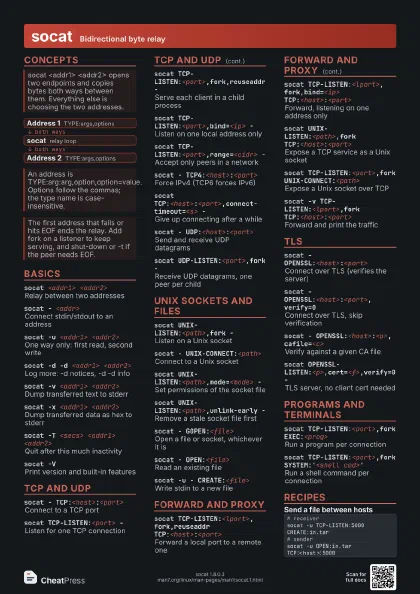
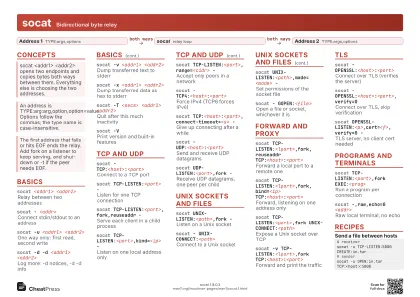
Concepts
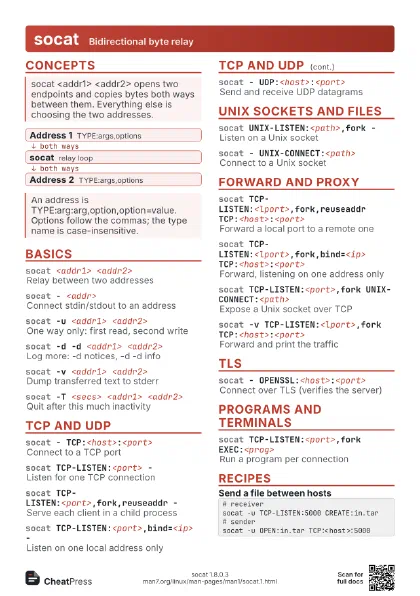
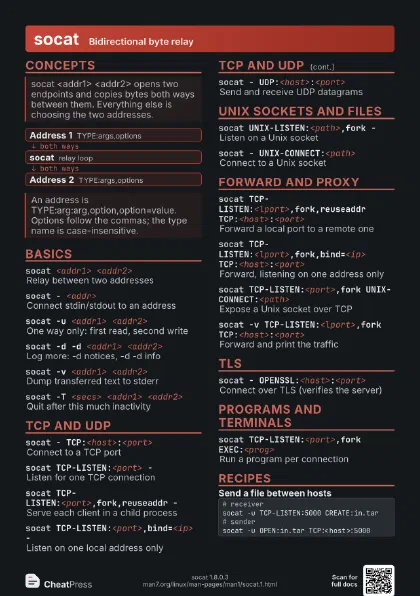
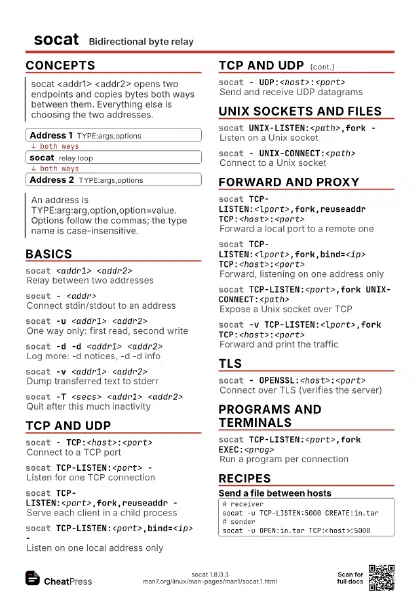
- Address 1 TYPE:args,options
- socat relay loop
- Address 2 TYPE:args,options
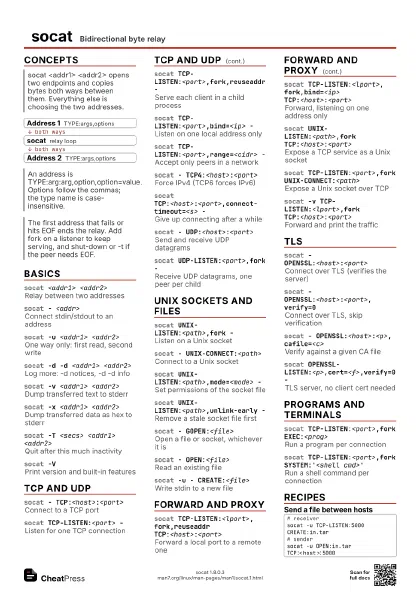
Basics
socat <addr1> <addr2>
Relay between two addresses
socat - <addr>
Connect stdin/stdout to an address
socat -u <addr1> <addr2>
One way only: first read, second write
socat -d -d <addr1> <addr2>
Log more: -d notices, -d -d info
socat -v <addr1> <addr2>
Dump transferred text to stderr
socat -x <addr1> <addr2>
Dump transferred data as hex to stderr
socat -T <secs> <addr1> <addr2>
Quit after this much inactivity
socat -VPrint version and built-in features
TCP and UDP
socat - TCP:<host>:<port>
Connect to a TCP port
socat TCP-LISTEN:<port> -
Listen for one TCP connection
socat TCP-LISTEN:<port>,fork,reuseaddr -
Serve each client in a child process
socat TCP-LISTEN:<port>,bind=<ip> -
Listen on one local address only
socat TCP-LISTEN:<port>,range=<cidr> -
Accept only peers in a network
socat - TCP4:<host>:<port>
Force IPv4 (TCP6 forces IPv6)
socat
                    TCP:<host>:<port>,connect-timeout=<s>
                    -
Give up connecting after a while
socat - UDP:<host>:<port>
Send and receive UDP datagrams
socat UDP-LISTEN:<port>,fork -
Receive UDP datagrams, one peer per child
Unix sockets and files
socat UNIX-LISTEN:<path>,fork -
Listen on a Unix socket
socat - UNIX-CONNECT:<path>
Connect to a Unix socket
socat UNIX-LISTEN:<path>,mode=<mode> -
Set permissions of the socket file
socat UNIX-LISTEN:<path>,unlink-early -
Remove a stale socket file first
socat - GOPEN:<file>
Open a file or socket, whichever it is
socat - OPEN:<file>
Read an existing file
socat -u - CREATE:<file>
Write stdin to a new file
socat -u - OPEN:<file>,creat,append
Append stdin to a file
Forward and proxy
socat TCP-LISTEN:<lport>,fork,reuseaddr
                    TCP:<host>:<port>
Forward a local port to a remote one
socat TCP-LISTEN:<lport>,fork,bind=<ip>
                    TCP:<host>:<port>
Forward, listening on one address only
socat UNIX-LISTEN:<path>,fork
                    TCP:<host>:<port>
Expose a TCP service as a Unix socket
socat TCP-LISTEN:<port>,fork
                    UNIX-CONNECT:<path>
Expose a Unix socket over TCP
socat TCP-LISTEN:<lport>,fork
                    PROXY:<proxy>:<host>:<port>
Connect through an HTTP proxy
socat TCP-LISTEN:<lport>,fork
                    SOCKS4A:<socks>:<host>:<port>
Connect through a SOCKS4A proxy
socat -v TCP-LISTEN:<lport>,fork
                    TCP:<host>:<port>
Forward and print the traffic
TLS
socat - OPENSSL:<host>:<port>
Connect over TLS (verifies the server)
socat - OPENSSL:<host>:<port>,verify=0
Connect over TLS, skip verification
socat -
                    OPENSSL:<host>:<p>,cafile=<c>
Verify against a given CA file
socat OPENSSL-LISTEN:<p>,cert=<f>,verify=0
                    -
TLS server, no client cert needed
Without verify=0 the server demands a client certificate.
<f> must hold key and cert, or add key=<key>.
socat
                    OPENSSL-LISTEN:<p>,cert=<f>,cafile=<c>
                    -
TLS server that requires client certs
socat -
                    OPENSSL:<host>:<port>,cert=<pem>
Present a client certificate
socat TCP-LISTEN:<lport>,fork
                    OPENSSL:<host>:<port>
Add TLS in front of a plain client
socat OPENSSL-LISTEN:<p>,cert=<f>,verify=0
                    TCP:<host>:<port>
Terminate TLS for a plain server
Programs and terminals
socat TCP-LISTEN:<port>,fork EXEC:<prog>
Run a program per connection
socat TCP-LISTEN:<port>,fork SYSTEM:'<shell
                    cmd>'
Run a shell command per connection
socat - EXEC:<prog>,pty,stderr
Run a program on a pty with stderr merged
socat -,raw,echo=0 EXEC:'bash
                    -i',pty,stderr,setsid
Full interactive shell over a pty
socat -,raw,echo=0 <addr>
Raw local terminal, no echo
socat PTY,link=<path>,raw,echo=0 <addr>
Create a pty device linked at a path
Recipes
# receiversocat -u TCP-LISTEN:5000 CREATE:in.tar# sendersocat -u OPEN:in.tar TCP:<host>:5000socat -v TCP-LISTEN:8080,fork \ TCP:example.com:80# other shellcurl localhost:8080/socat -v UNIX-LISTEN:s.sock,\ mode=600,fork \ UNIX-CONNECT:/run/docker.sock# then, in another shellcurl --unix-socket s.sock \ http://localhost/versionopenssl req -x509 -newkey \ rsa:2048 -nodes -subj \ /CN=localhost \ -keyout k.pem -out c.pemcat k.pem c.pem > both.pemsocat OPENSSL-LISTEN:4433,\ cert=both.pem,verify=0,fork -# other shellsocat - OPENSSL:localhost:4433,\ verify=0