Cheat
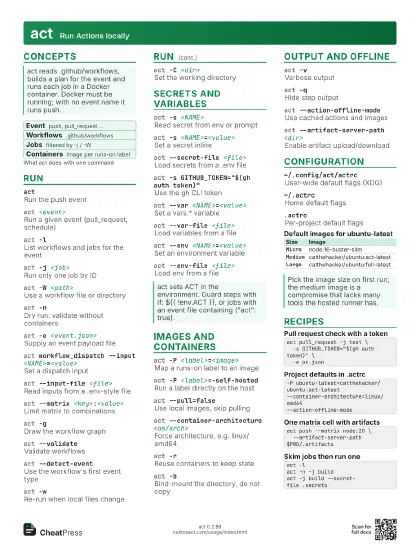
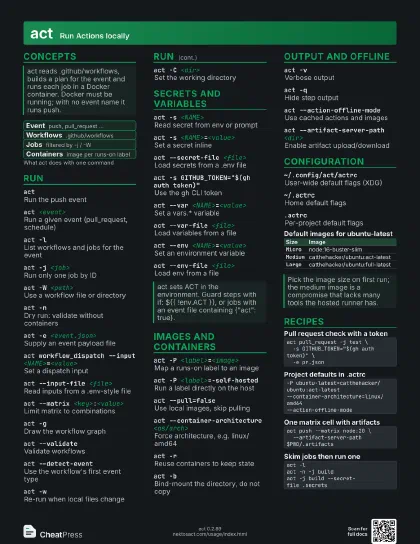
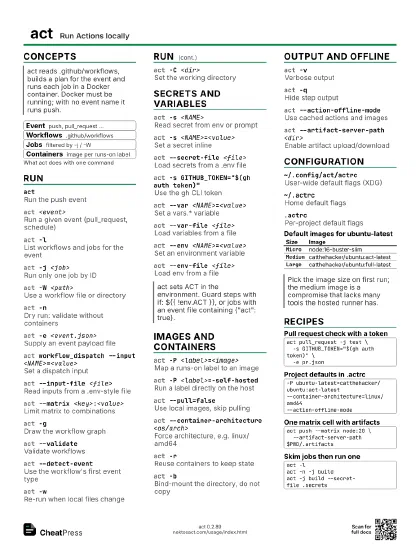
act Run Actions locally
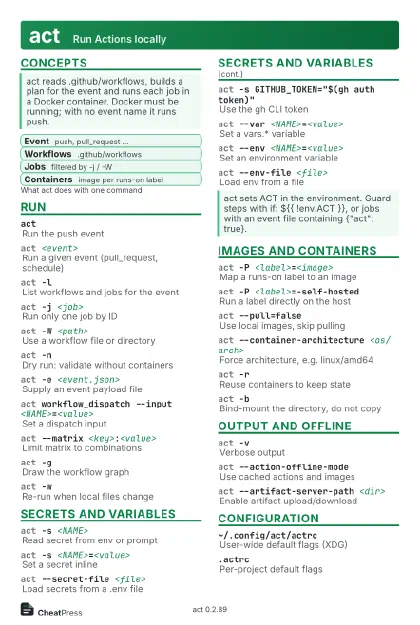 Light · Postcard
102 × 152 mm · PDF
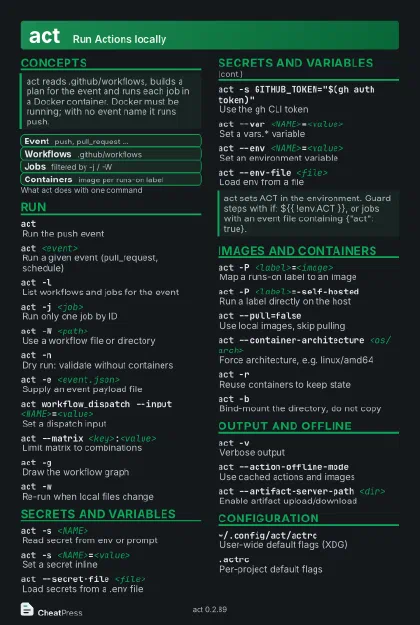 Dark · Postcard
102 × 152 mm · PDF
 Ink saver · Postcard
102 × 152 mm · PDF
 Light · A4 landscape
297 × 210 mm · PDF
 Dark · A4 landscape
297 × 210 mm · PDF
 Ink saver · A4 landscape
297 × 210 mm · PDF
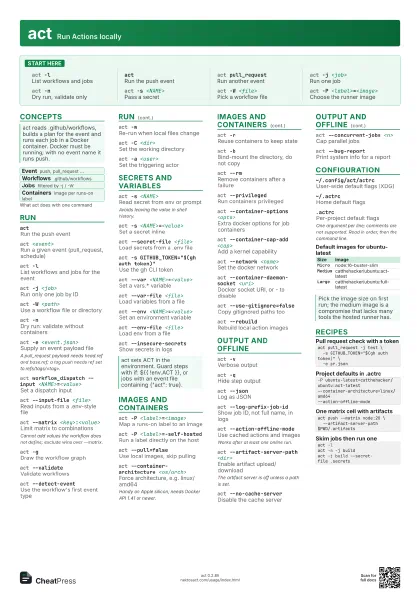
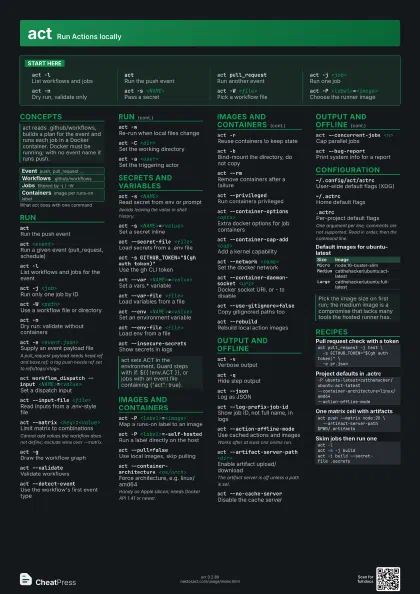
 Light · A3 landscape
420 × 297 mm · PDF
 Dark · A3 landscape
420 × 297 mm · PDF
 Ink saver · A3 landscape
420 × 297 mm · PDF
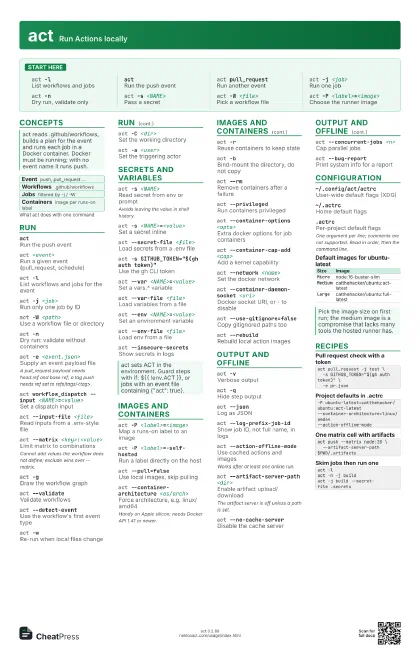
Start here
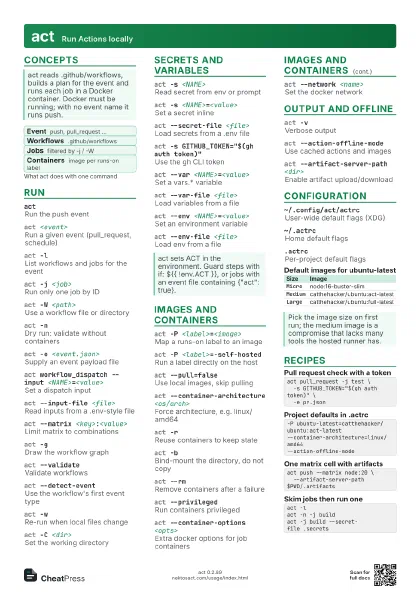
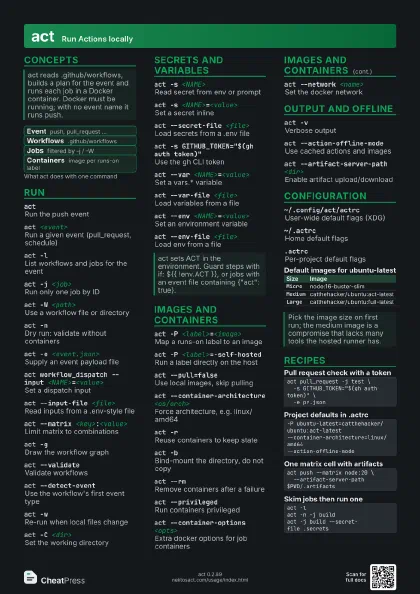
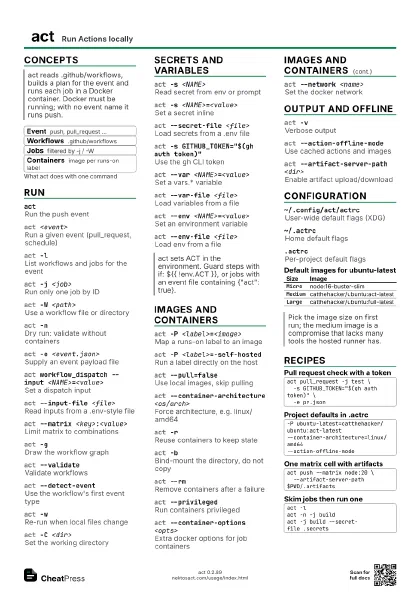
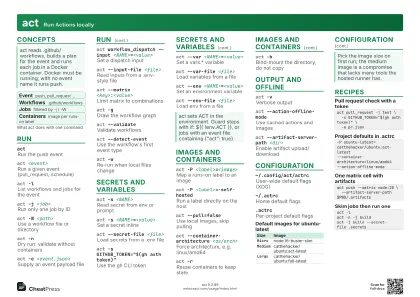
act -lList workflows and jobs
actRun the push event
act pull_request
Run another event
act -j <job>
Run one job
act -nDry run, validate only
act -s <NAME>
Pass a secret
act -W <file>
Pick a workflow file
act -P <label>=<image>
Choose the runner image
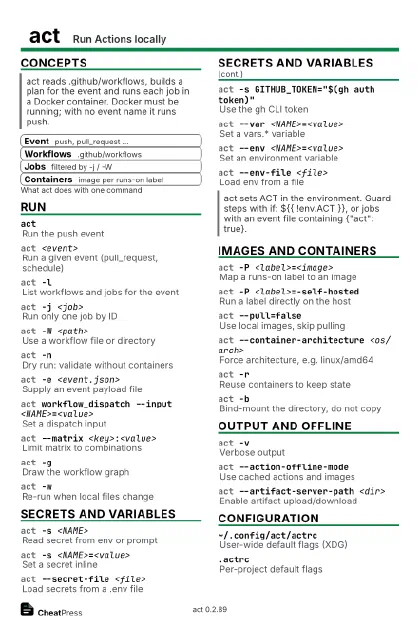
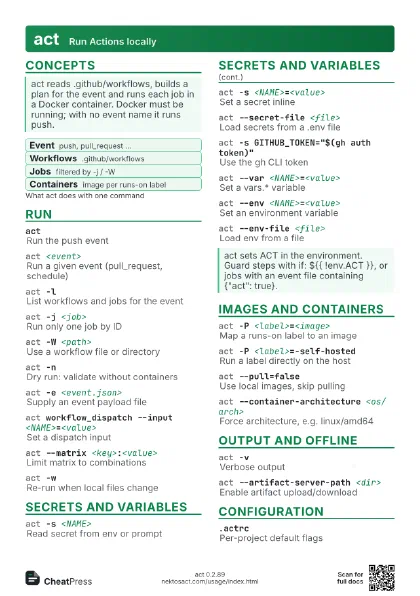
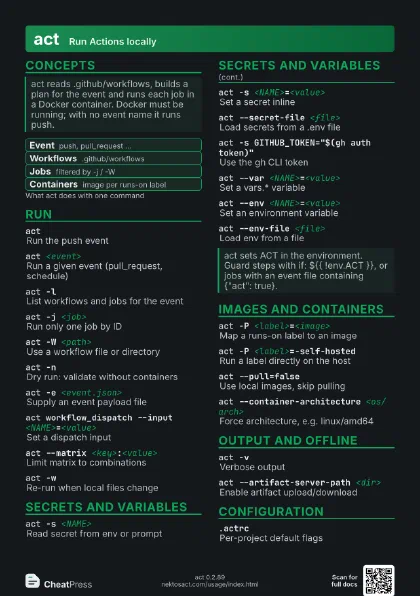
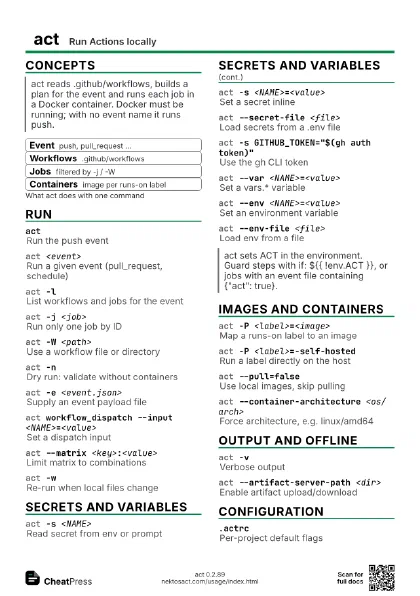
Concepts
- Event push, pull_request ...
- Workflows .github/workflows
- Jobs filtered by -j / -W
- Containers image per runs-on label
Run
actRun the push event
act <event>
Run a given event (pull_request, schedule)
act -lList workflows and jobs for the event
act -j <job>
Run only one job by ID
act -W <path>
Use a workflow file or directory
act -nDry run: validate without containers
act -e <event.json>
Supply an event payload file
A pull_request payload needs head.ref and base.ref; a tag push
needs ref set to refs/tags/<tag>.
act workflow_dispatch --input
                    <NAME>=<value>
Set a dispatch input
act --input-file <file>
Read inputs from a .env-style file
act --matrix <key>:<value>
Limit matrix to combinations
Cannot add values the workflow does not define; exclude wins
over --matrix.
act -gDraw the workflow graph
act --validateValidate workflows
act --detect-event
Use the workflow's first event type
act -wRe-run when local files change
act -C <dir>
Set the working directory
act -a <user>
Set the triggering actor
Secrets and variables
act -s <NAME>
Read secret from env or prompt
Avoids leaving the value in shell history.
act -s <NAME>=<value>
Set a secret inline
act --secret-file <file>
Load secrets from a .env file
act -s GITHUB_TOKEN="$(gh auth token)"
Use the gh CLI token
act --var <NAME>=<value>
Set a vars.* variable
act --var-file <file>
Load variables from a file
act --env <NAME>=<value>
Set an environment variable
act --env-file <file>
Load env from a file
act --insecure-secrets
Show secrets in logs
Images and containers
act -P <label>=<image>
Map a runs-on label to an image
act -P <label>=-self-hosted
Run a label directly on the host
act --pull=false
Use local images, skip pulling
act --container-architecture <os/arch>
Force architecture, e.g. linux/amd64
Handy on Apple silicon; needs Docker API 1.41 or newer.
act -rReuse containers to keep state
act -bBind-mount the directory, do not copy
act --rmRemove containers after a failure
act --privileged
Run containers privileged
act --container-options <opts>
Extra docker options for job containers
act --container-cap-add <cap>
Add a kernel capability
act --network <name>
Set the docker network
act --container-daemon-socket <uri>
Docker socket URI, or - to disable
act --use-gitignore=false
Copy gitignored paths too
act --rebuildRebuild local action images
Output and offline
act -vVerbose output
act -qHide step output
act --jsonLog as JSON
act --log-prefix-job-id
Show job ID, not full name, in logs
act --action-offline-mode
Use cached actions and images
Works after at least one online run.
act --artifact-server-path <dir>
Enable artifact upload/download
The artifact server is off unless a path is set.
act --no-cache-server
Disable the cache server
act --concurrent-jobs <n>
Cap parallel jobs
act --bug-report
Print system info for a report
Configuration
~/.config/act/actrc
User-wide default flags (XDG)
~/.actrcHome default flags
.actrcPer-project default flags
One argument per line; comments are not supported. Read in
order, then the command line.
| Size | Image |
|---|---|
Micro |
node:16-buster-slim |
Medium |
catthehacker/ubuntu:act-latest |
Large |
catthehacker/ubuntu:full-latest |
Recipes
act pull_request -j test \ -s GITHUB_TOKEN="$(gh auth token)" \ -e pr.json-P ubuntu-latest=catthehacker/ubuntu:act-latest--container-architecture=linux/amd64--action-offline-modeact push --matrix node:20 \ --artifact-server-path $PWD/.artifactsact -lact -n -j buildact -j build --secret-file .secrets