Cheat
mkcert Local trusted dev certs
 Light · Postcard
102 × 152 mm · PDF
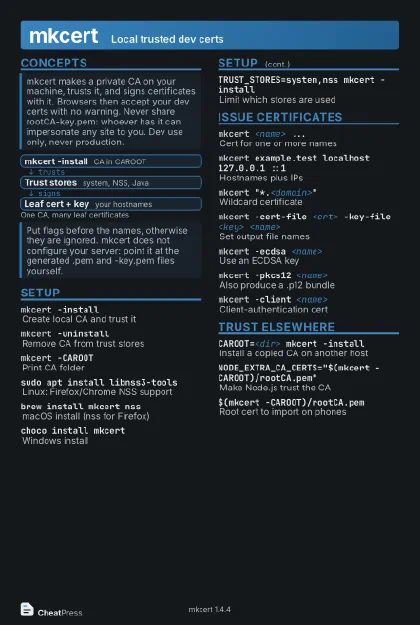 Dark · Postcard
102 × 152 mm · PDF
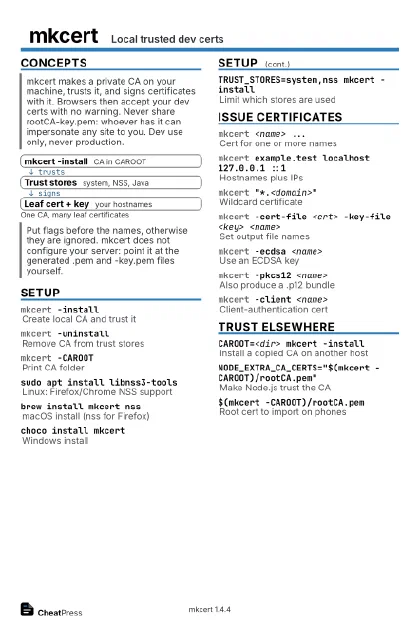 Ink saver · Postcard
102 × 152 mm · PDF
 Light · A4 landscape
297 × 210 mm · PDF
 Dark · A4 landscape
297 × 210 mm · PDF
 Ink saver · A4 landscape
297 × 210 mm · PDF
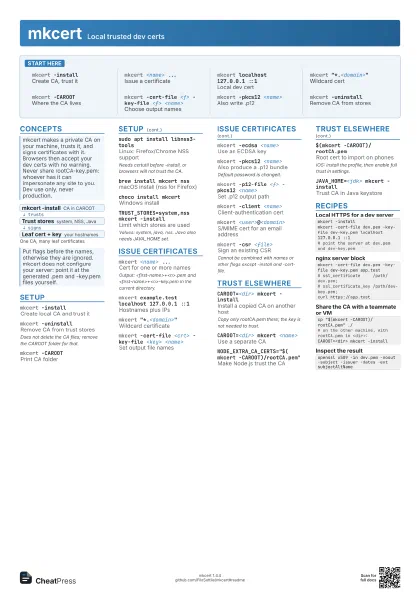
 Light · A3 landscape
420 × 297 mm · PDF
 Dark · A3 landscape
420 × 297 mm · PDF
 Ink saver · A3 landscape
420 × 297 mm · PDF
Start here
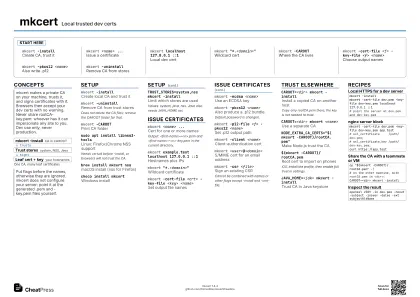
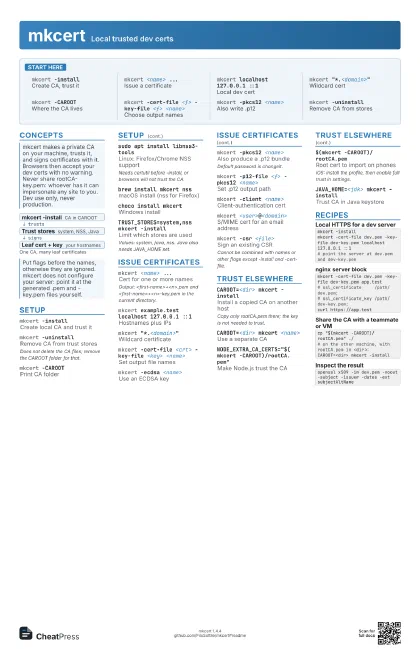
mkcert -installCreate CA, trust it
mkcert <name> ...
Issue a certificate
mkcert localhost 127.0.0.1 ::1
Local dev cert
mkcert "*.<domain>"
Wildcard cert
mkcert -CAROOTWhere the CA lives
mkcert -cert-file <f> -key-file <f>
                    <name>
Choose output names
mkcert -pkcs12 <name>
Also write .p12
mkcert -uninstall
Remove CA from stores
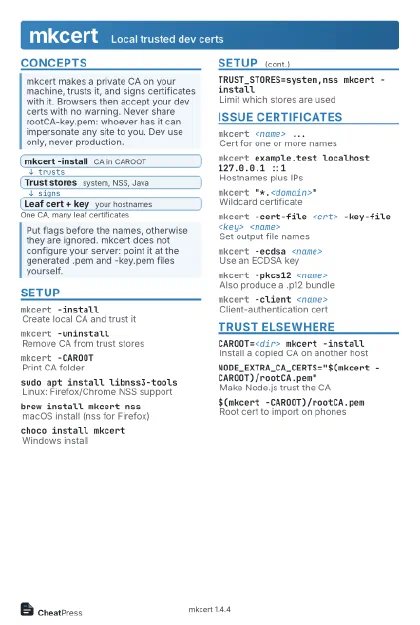
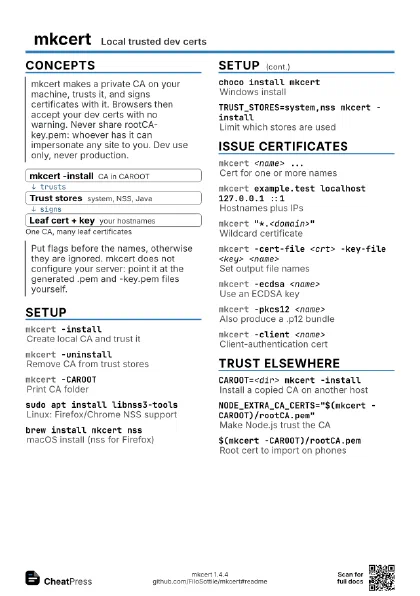
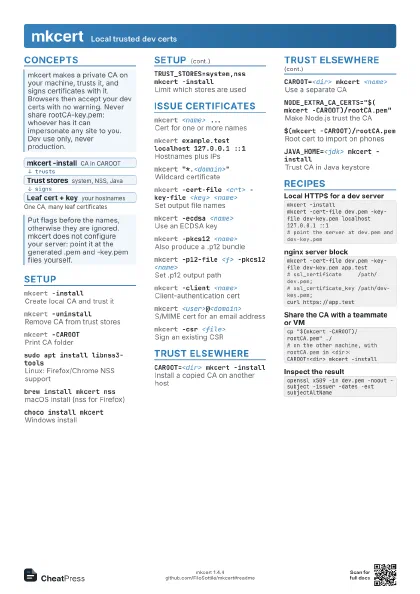
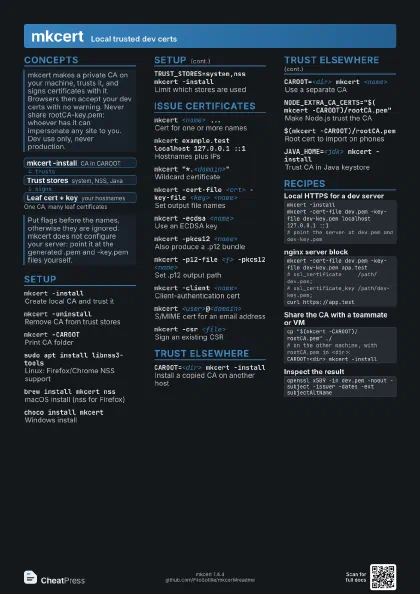
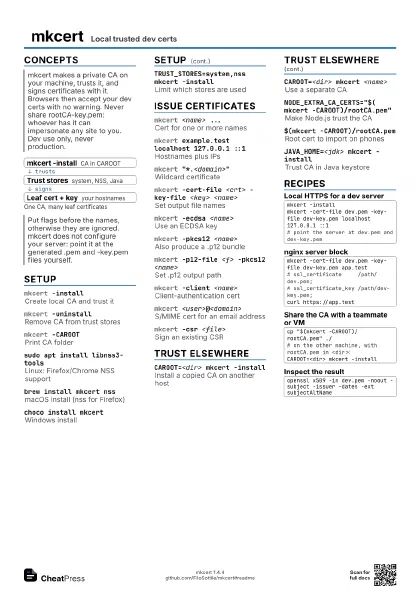
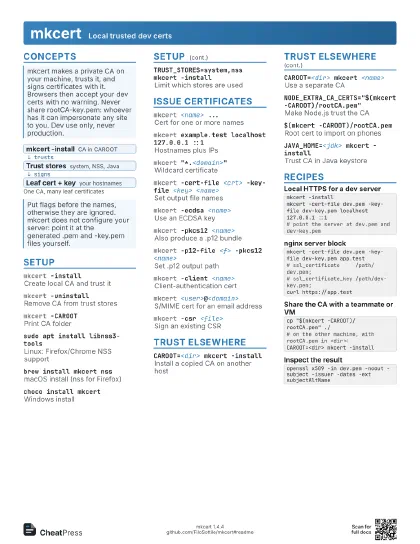
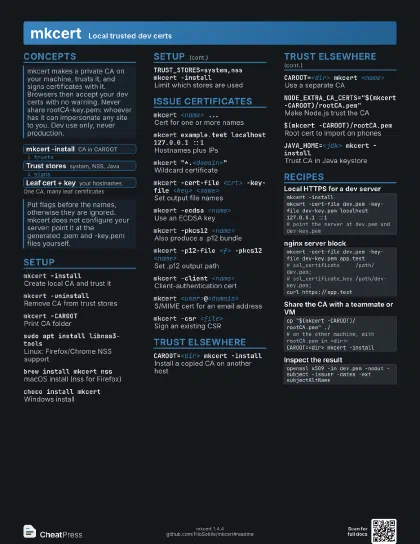
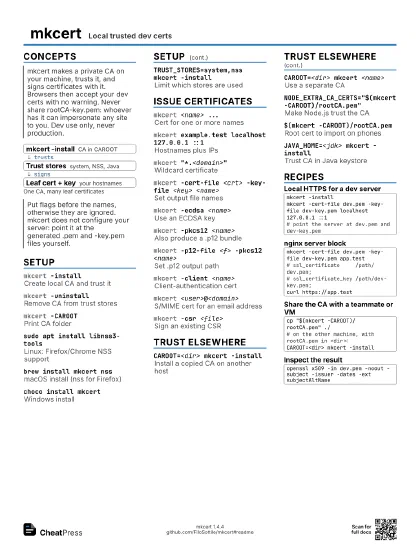
Concepts
- mkcert -install CA in CAROOT
- Trust stores system, NSS, Java
- Leaf cert + key your hostnames
Setup
mkcert -installCreate local CA and trust it
mkcert -uninstall
Remove CA from trust stores
Does not delete the CA files; remove the CAROOT folder for
that.
mkcert -CAROOTPrint CA folder
sudo apt install libnss3-tools
Linux: Firefox/Chrome NSS support
Needs certutil before -install, or browsers will not trust the
CA.
brew install mkcert nss
macOS install (nss for Firefox)
choco install mkcert
Windows install
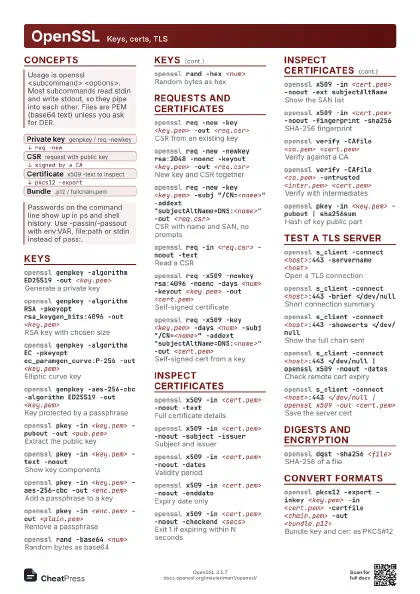
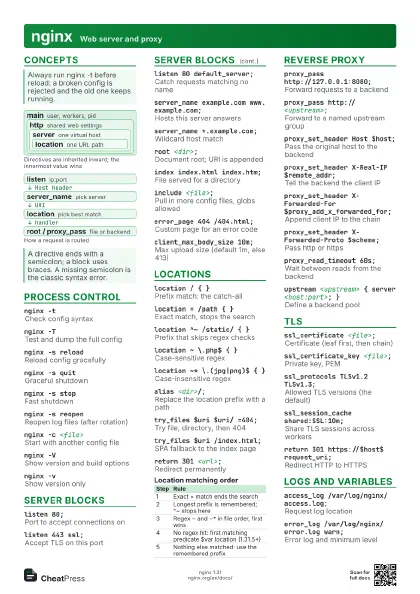
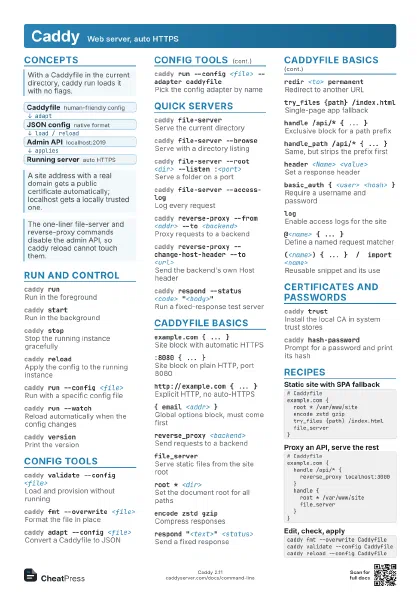
TRUST_STORES=system,nss mkcert -install
Limit which stores are used
Values: system, java, nss. Java also needs JAVA_HOME set.
Issue certificates
mkcert <name> ...
Cert for one or more names
Output: <first-name>+<n>.pem and
<first-name>+<n>-key.pem in the current
directory.
mkcert example.test localhost 127.0.0.1 ::1
Hostnames plus IPs
mkcert "*.<domain>"
Wildcard certificate
mkcert -cert-file <crt> -key-file <key>
                    <name>
Set output file names
mkcert -ecdsa <name>
Use an ECDSA key
mkcert -pkcs12 <name>
Also produce a .p12 bundle
Default password is changeit.
mkcert -p12-file <f> -pkcs12 <name>
Set .p12 output path
mkcert -client <name>
Client-authentication cert
mkcert <user>@<domain>
S/MIME cert for an email address
mkcert -csr <file>
Sign an existing CSR
Cannot be combined with names or other flags except -install
and -cert-file.
Trust elsewhere
CAROOT=<dir> mkcert -install
Install a copied CA on another host
Copy only rootCA.pem there; the key is not needed to trust.
CAROOT=<dir> mkcert <name>
Use a separate CA
NODE_EXTRA_CA_CERTS="$(mkcert
                    -CAROOT)/rootCA.pem"
Make Node.js trust the CA
$(mkcert -CAROOT)/rootCA.pem
Root cert to import on phones
iOS: install the profile, then enable full trust in settings.
JAVA_HOME=<jdk> mkcert -install
Trust CA in Java keystore
Recipes
mkcert -installmkcert -cert-file dev.pem -key-file dev-key.pem localhost 127.0.0.1 ::1# point the server at dev.pem and dev-key.pemmkcert -cert-file dev.pem -key-file dev-key.pem app.test# ssl_certificate /path/dev.pem;# ssl_certificate_key /path/dev-key.pem;curl https://app.testcp "$(mkcert -CAROOT)/rootCA.pem" ./# on the other machine, with rootCA.pem in <dir>:CAROOT=<dir> mkcert -installopenssl x509 -in dev.pem -noout -subject -issuer -dates -ext subjectAltName