Cheat
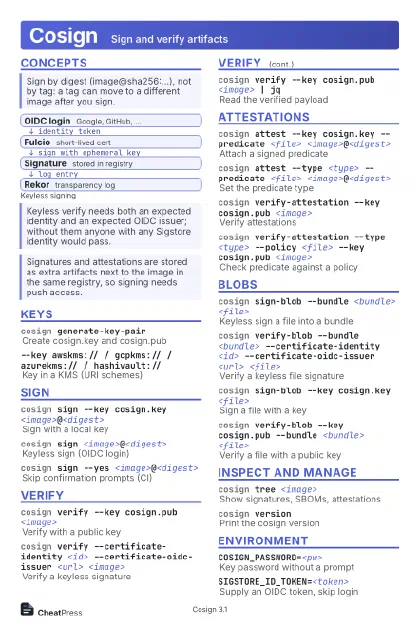
Cosign Sign and verify artifacts
 Light · Postcard
102 × 152 mm · PDF
 Dark · Postcard
102 × 152 mm · PDF
 Ink saver · Postcard
102 × 152 mm · PDF
 Light · A4 landscape
297 × 210 mm · PDF
 Dark · A4 landscape
297 × 210 mm · PDF
 Ink saver · A4 landscape
297 × 210 mm · PDF
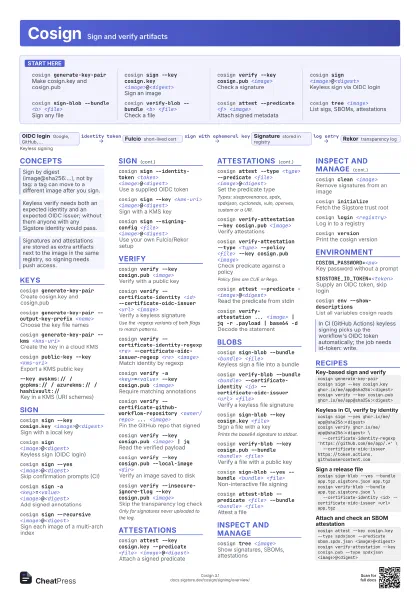
 Light · A3 landscape
420 × 297 mm · PDF
 Dark · A3 landscape
420 × 297 mm · PDF
 Ink saver · A3 landscape
420 × 297 mm · PDF
Start here
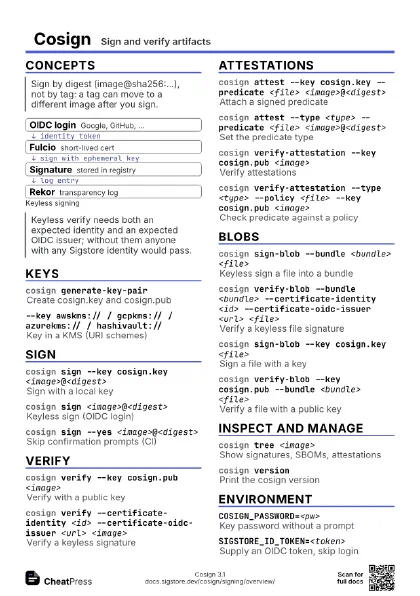
cosign generate-key-pair
Make cosign.key and cosign.pub
cosign sign --key cosign.key
                    <image>@<digest>
Sign an image
cosign verify --key cosign.pub <image>
Check a signature
cosign sign <image>@<digest>
Keyless sign via OIDC login
cosign sign-blob --bundle <b> <file>
Sign any file
cosign verify-blob --bundle <b> <file>
Check a file
cosign attest --predicate <f> <image>
Attach signed metadata
cosign tree <image>
List sigs, SBOMs, attestations
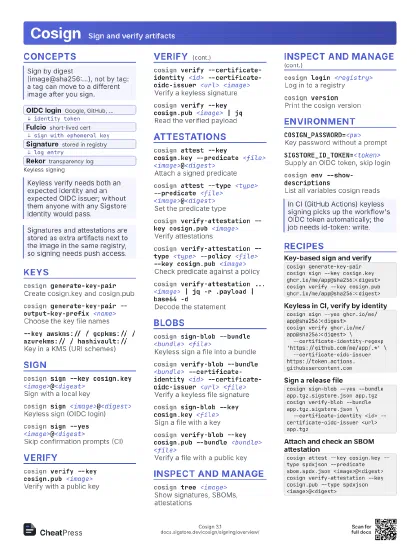
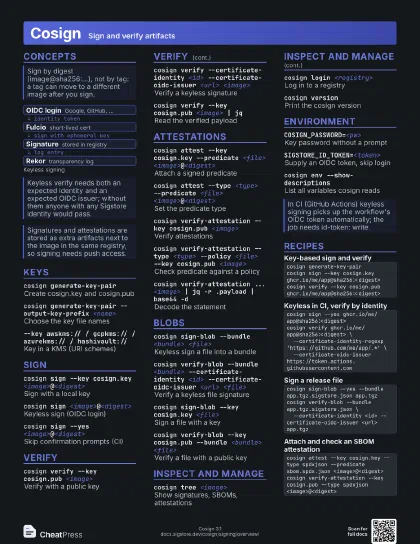
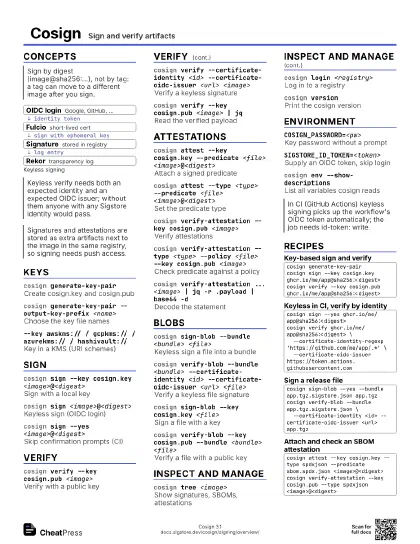
Concepts
- OIDC login Google, GitHub, ...
- Fulcio short-lived cert
- Signature stored in registry
- Rekor transparency log
Keys
cosign generate-key-pair
Create cosign.key and cosign.pub
cosign generate-key-pair --output-key-prefix
                    <name>
Choose the key file names
cosign generate-key-pair --kms <kms-uri>
Create the key in a cloud KMS
cosign public-key --key <kms-uri>
Export a KMS public key
--key awskms:// / gcpkms:// / azurekms:// /
                    hashivault://
Key in a KMS (URI schemes)
Sign
cosign sign --key cosign.key
                    <image>@<digest>
Sign with a local key
cosign sign <image>@<digest>
Keyless sign (OIDC login)
cosign sign --yes <image>@<digest>
Skip confirmation prompts (CI)
cosign sign -a <key>=<value>
                    <image>@<digest>
Add signed annotations
cosign sign --recursive <image>@<digest>
Sign each image of a multi-arch index
cosign sign --identity-token <token>
                    <image>@<digest>
Use a supplied OIDC token
cosign sign --key <kms-uri>
                    <image>@<digest>
Sign with a KMS key
cosign sign --signing-config <file>
                    <image>@<digest>
Use your own Fulcio/Rekor setup
Verify
cosign verify --key cosign.pub <image>
Verify with a public key
cosign verify --certificate-identity <id>
                    --certificate-oidc-issuer <url> <image>
Verify a keyless signature
Use the -regexp variants of both flags to match patterns.
cosign verify --certificate-identity-regexp <re>
                    --certificate-oidc-issuer-regexp <re>
                    <image>
Match identity by regexp
cosign verify -a <key>=<value> --key cosign.pub
                    <image>
Require matching annotations
cosign verify --certificate-github-workflow-repository
                    <owner/repo> ... <image>
Pin the GitHub repo that signed
cosign verify --key cosign.pub <image> | jq
Read the verified payload
cosign verify --key cosign.pub --local-image
                    <dir>
Verify an image saved to disk
cosign verify --insecure-ignore-tlog --key cosign.pub
                    <image>
Skip the transparency log check
Only for signatures never uploaded to the log.
Attestations
cosign attest --key cosign.key --predicate <file>
                    <image>@<digest>
Attach a signed predicate
cosign attest --type <type> --predicate <file>
                    <image>@<digest>
Set the predicate type
Types: slsaprovenance, spdx, spdxjson, cyclonedx, vuln,
openvex, custom or a URI.
cosign verify-attestation --key cosign.pub
                    <image>
Verify attestations
cosign verify-attestation --type <type> --policy
                    <file> --key cosign.pub <image>
Check predicate against a policy
Policy files are CUE or Rego.
cosign attest --predicate -
                    <image>@<digest>
Read the predicate from stdin
cosign verify-attestation ... <image> | jq -r
                    .payload | base64 -d
Decode the statement
Blobs
cosign sign-blob --bundle <bundle> <file>
Keyless sign a file into a bundle
cosign verify-blob --bundle <bundle>
                    --certificate-identity <id> --certificate-oidc-issuer
                    <url> <file>
Verify a keyless file signature
cosign sign-blob --key cosign.key <file>
Sign a file with a key
Prints the base64 signature to stdout.
cosign verify-blob --key cosign.pub --bundle <bundle>
                    <file>
Verify a file with a public key
cosign sign-blob --yes --bundle <bundle>
                    <file>
Non-interactive file signing
cosign attest-blob --predicate <file> --bundle
                    <bundle> <file>
Attest a file
Inspect and manage
cosign tree <image>
Show signatures, SBOMs, attestations
cosign save --dir <dir> <image>
Save image and signatures to disk
cosign load --dir <dir> <image>
Upload a saved image to a registry
cosign clean <image>
Remove signatures from an image
cosign initialize
Fetch the Sigstore trust root
cosign login <registry>
Log in to a registry
cosign versionPrint the cosign version
Environment
COSIGN_PASSWORD=<pw>
Key password without a prompt
SIGSTORE_ID_TOKEN=<token>
Supply an OIDC token, skip login
SIGSTORE_ROOT_FILE=<pem>
Use a custom root certificate
cosign env --show-descriptions
List all variables cosign reads
Recipes
cosign generate-key-paircosign sign --key cosign.key ghcr.io/me/app@sha256:<digest>cosign verify --key cosign.pub ghcr.io/me/app@sha256:<digest>cosign sign --yes ghcr.io/me/app@sha256:<digest>cosign verify ghcr.io/me/app@sha256:<digest> \ --certificate-identity-regexp 'https://github.com/me/app/.*' \ --certificate-oidc-issuer https://token.actions.githubusercontent.comcosign sign-blob --yes --bundle app.tgz.sigstore.json app.tgzcosign verify-blob --bundle app.tgz.sigstore.json \ --certificate-identity <id> --certificate-oidc-issuer <url> app.tgzcosign attest --key cosign.key --type spdxjson --predicate sbom.spdx.json <image>@<digest>cosign verify-attestation --key cosign.pub --type spdxjson <image>@<digest>