Cheat
Consul Service discovery and KV
 Light · Postcard
102 × 152 mm · PDF
 Dark · Postcard
102 × 152 mm · PDF
 Ink saver · Postcard
102 × 152 mm · PDF
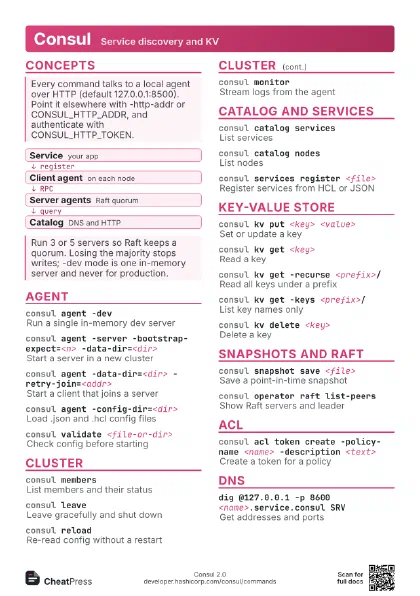
 Light · A4 landscape
297 × 210 mm · PDF
 Dark · A4 landscape
297 × 210 mm · PDF
 Ink saver · A4 landscape
297 × 210 mm · PDF
 Light · A3 landscape
420 × 297 mm · PDF
 Dark · A3 landscape
420 × 297 mm · PDF
 Ink saver · A3 landscape
420 × 297 mm · PDF
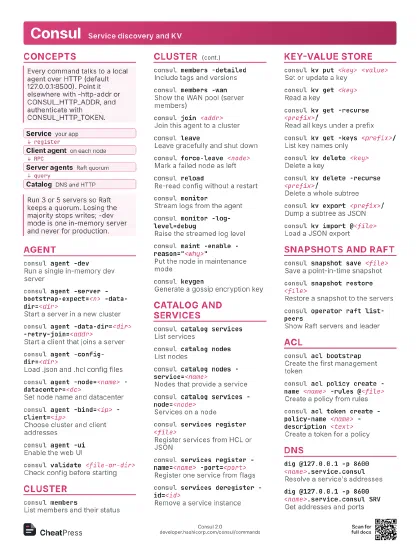
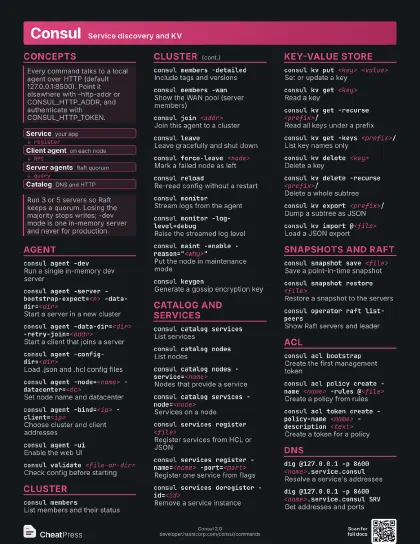
Start here
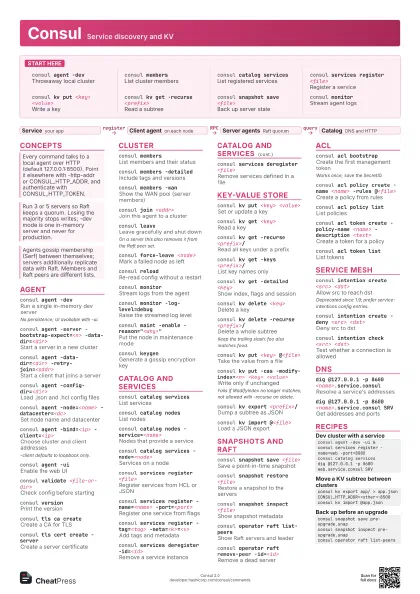
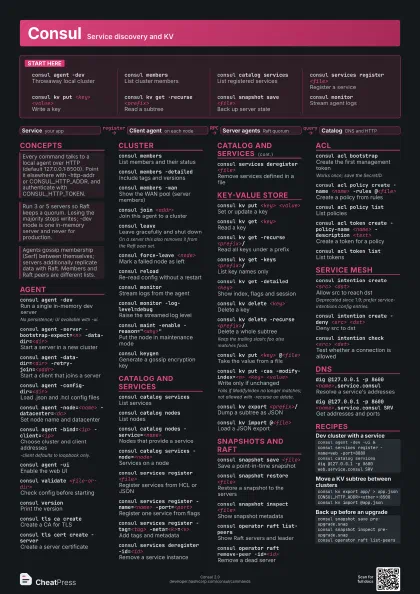
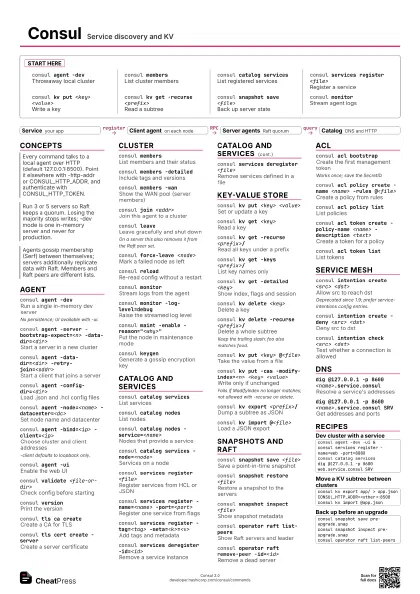
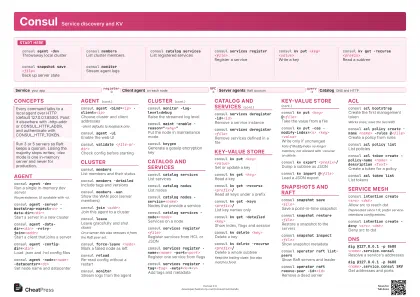
consul agent -dev
Throwaway local cluster
consul membersList cluster members
consul catalog services
List registered services
consul services register <file>
Register a service
consul kv put <key> <value>
Write a key
consul kv get -recurse <prefix>
Read a subtree
consul snapshot save <file>
Back up server state
consul monitorStream agent logs
Concepts
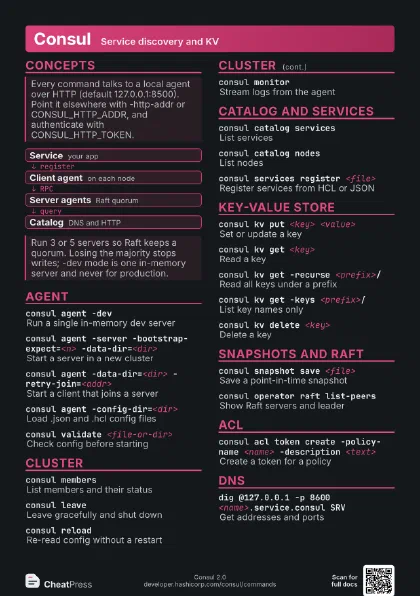
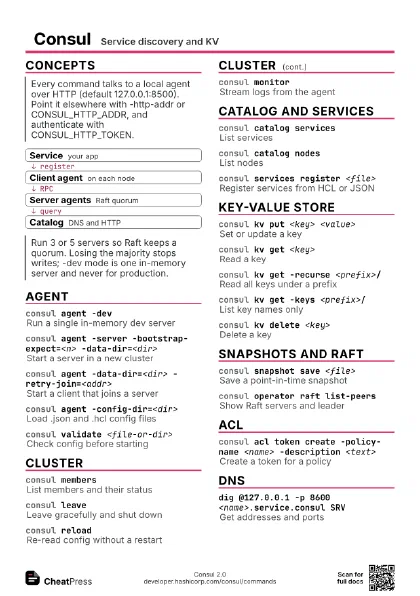
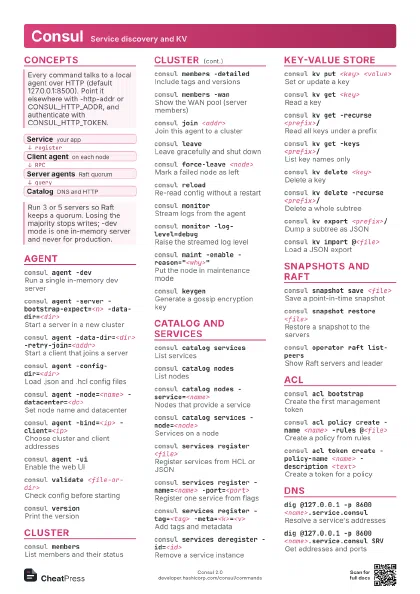
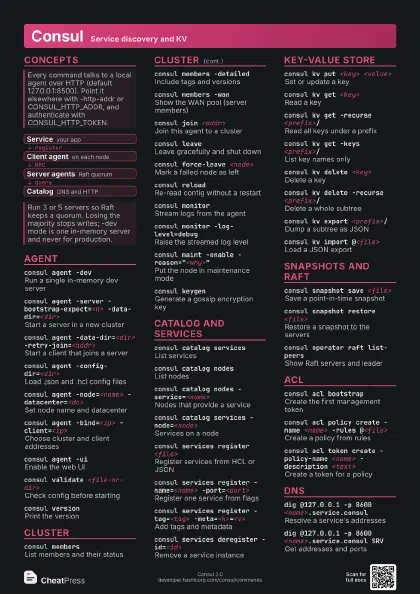
- Service your app
- Client agent on each node
- Server agents Raft quorum
- Catalog DNS and HTTP
Agent
consul agent -dev
Run a single in-memory dev server
No persistence; UI available with -ui.
consul agent -server -bootstrap-expect=<n>
                    -data-dir=<dir>
Start a server in a new cluster
consul agent -data-dir=<dir>
                    -retry-join=<addr>
Start a client that joins a server
consul agent -config-dir=<dir>
Load .json and .hcl config files
consul agent -node=<name>
                    -datacenter=<dc>
Set node name and datacenter
consul agent -bind=<ip> -client=<ip>
Choose cluster and client addresses
-client defaults to loopback only.
consul agent -ui
Enable the web UI
consul validate <file-or-dir>
Check config before starting
consul versionPrint the version
consul tls ca create
Create a CA for TLS
consul tls cert create -server
Create a server certificate
Cluster
consul membersList members and their status
consul members -detailed
Include tags and versions
consul members -wan
Show the WAN pool (server members)
consul join <addr>
Join this agent to a cluster
consul leaveLeave gracefully and shut down
On a server this also removes it from the Raft peer set.
consul force-leave <node>
Mark a failed node as left
consul reloadRe-read config without a restart
consul monitorStream logs from the agent
consul monitor -log-level=debug
Raise the streamed log level
consul maint -enable -reason="<why>"
Put the node in maintenance mode
consul keygenGenerate a gossip encryption key
Catalog and services
consul catalog services
List services
consul catalog nodes
List nodes
consul catalog nodes -service=<name>
Nodes that provide a service
consul catalog services -node=<node>
Services on a node
consul services register <file>
Register services from HCL or JSON
consul services register -name=<name>
                    -port=<port>
Register one service from flags
consul services register -tag=<tag>
                    -meta=<k>=<v>
Add tags and metadata
consul services deregister -id=<id>
Remove a service instance
consul services deregister <file>
Remove services defined in a file
Key-value store
consul kv put <key> <value>
Set or update a key
consul kv get <key>
Read a key
consul kv get -recurse <prefix>/
Read all keys under a prefix
consul kv get -keys <prefix>/
List key names only
consul kv get -detailed <key>
Show index, flags and session
consul kv delete <key>
Delete a key
consul kv delete -recurse <prefix>/
Delete a whole subtree
Keep the trailing slash: foo also matches food.
consul kv put <key> @<file>
Take the value from a file
consul kv put -cas -modify-index=<n> <key>
                    <value>
Write only if unchanged
Fails if ModifyIndex no longer matches; not allowed with
-recurse on delete.
consul kv export <prefix>/
Dump a subtree as JSON
consul kv import @<file>
Load a JSON export
consul lock <prefix> <command>
Run a command while holding a lock
Snapshots and Raft
consul snapshot save <file>
Save a point-in-time snapshot
consul snapshot restore <file>
Restore a snapshot to the servers
consul snapshot inspect <file>
Show snapshot metadata
consul operator raft list-peers
Show Raft servers and leader
consul operator raft list-peers -stale=true
List peers when there is no leader
consul operator raft remove-peer -id=<id>
Remove a dead server
consul operator raft transfer-leader
Hand leadership to another server
ACL
consul acl bootstrap
Create the first management token
Works once; save the SecretID.
consul acl policy create -name <name> -rules
                    @<file>
Create a policy from rules
consul acl policy list
List policies
consul acl token create -policy-name <name>
                    -description <text>
Create a token for a policy
consul acl token list
List tokens
consul acl set-agent-token <type> <token>
Give the agent its own token
Service mesh
consul intention create <src> <dst>
Allow src to reach dst
Deprecated since 1.9; prefer service-intentions config
entries.
consul intention create -deny <src> <dst>
Deny src to dst
consul intention check <src> <dst>
Test whether a connection is allowed
consul connect envoy -sidecar-for <id>
Start an Envoy sidecar
DNS
dig @127.0.0.1 -p 8600 <name>.service.consul
Resolve a service's addresses
dig @127.0.0.1 -p 8600 <name>.service.consul
                    SRV
Get addresses and ports
dig @127.0.0.1 -p 8600
                    <tag>.<name>.service.consul
Resolve by tag
dig @127.0.0.1 -p 8600 <node>.node.consul
Resolve a node
Recipes
consul agent -dev -ui &consul services register -name=web -port=8080consul catalog servicesdig @127.0.0.1 -p 8600 web.service.consul SRVconsul kv export app/ > app.jsonCONSUL_HTTP_ADDR=<other>:8500 consul kv import @app.jsonconsul snapshot save pre-upgrade.snapconsul snapshot inspect pre-upgrade.snapconsul operator raft list-peers{ "service": { "name": "web", "port": 8080, "tags": ["v1"] }}