Cheat
Apache HTTP Server Web server
 Light · Postcard
102 × 152 mm · PDF
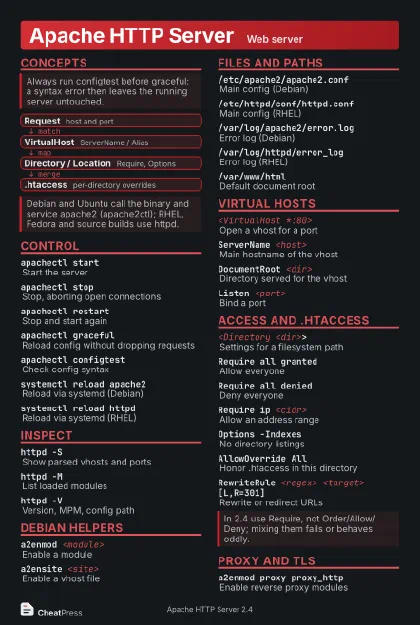 Dark · Postcard
102 × 152 mm · PDF
 Ink saver · Postcard
102 × 152 mm · PDF
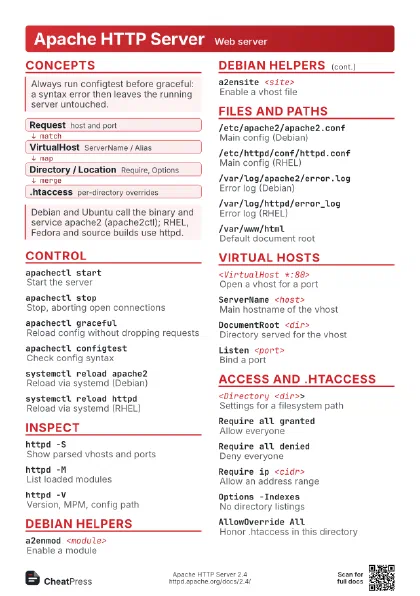
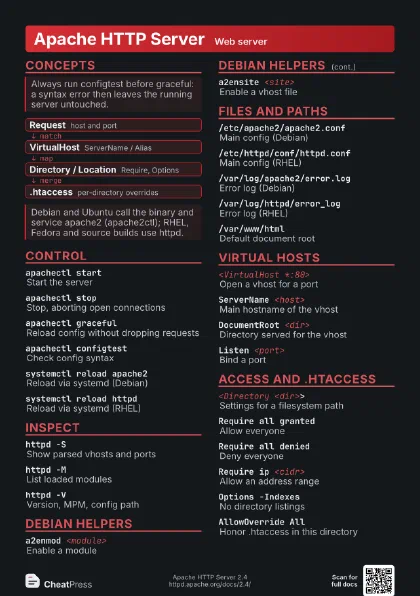
 Light · A4 landscape
297 × 210 mm · PDF
 Dark · A4 landscape
297 × 210 mm · PDF
 Ink saver · A4 landscape
297 × 210 mm · PDF
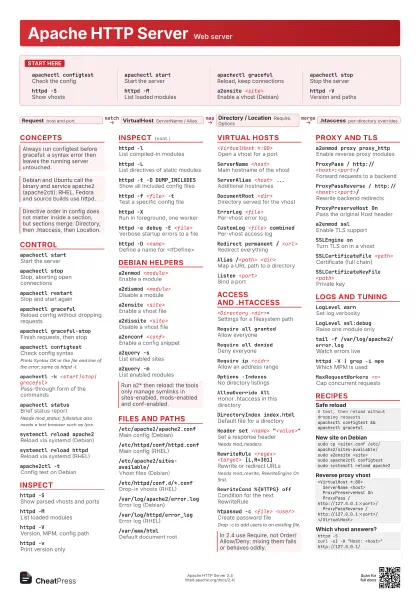
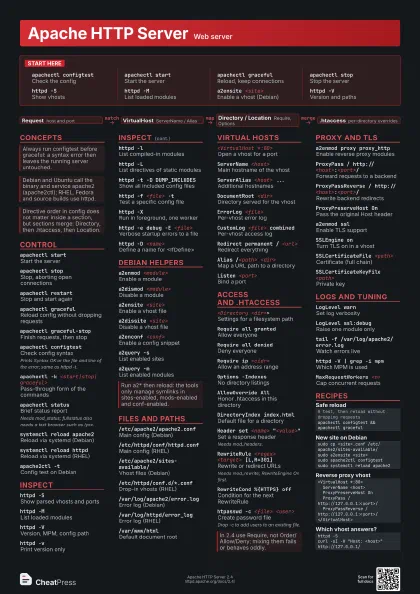
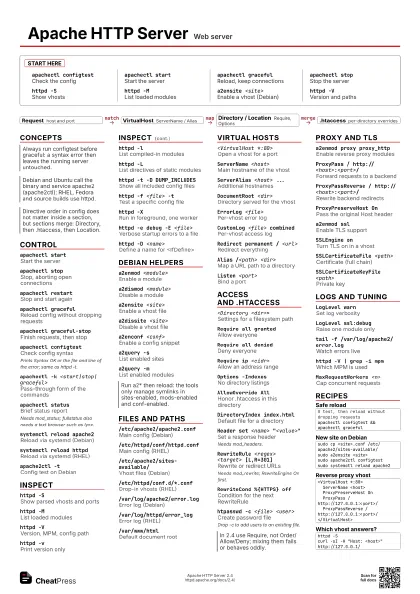
 Light · A3 landscape
420 × 297 mm · PDF
 Dark · A3 landscape
420 × 297 mm · PDF
 Ink saver · A3 landscape
420 × 297 mm · PDF
Start here
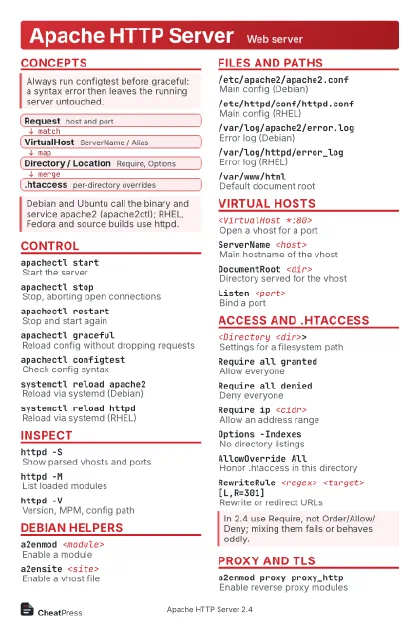
apachectl configtest
Check the config
apachectl startStart the server
apachectl graceful
Reload, keep connections
apachectl stopStop the server
httpd -SShow vhosts
httpd -MList loaded modules
a2ensite <site>
Enable a vhost (Debian)
httpd -VVersion and paths
Concepts
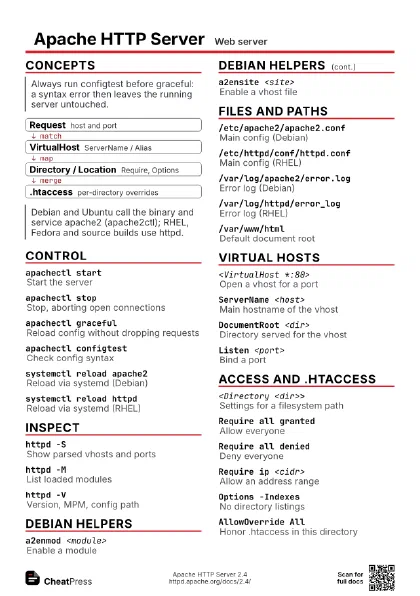
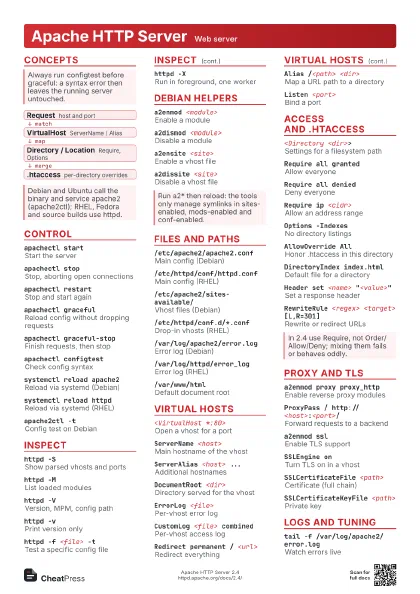
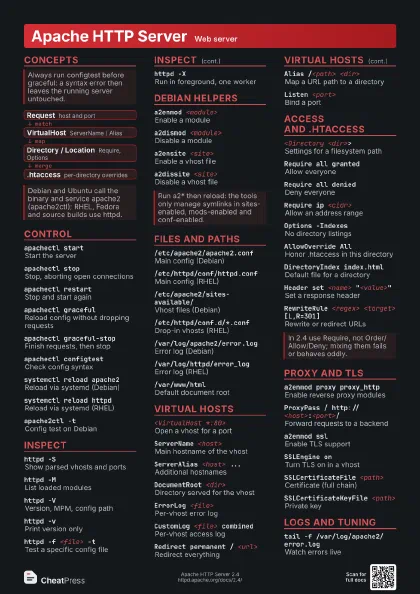
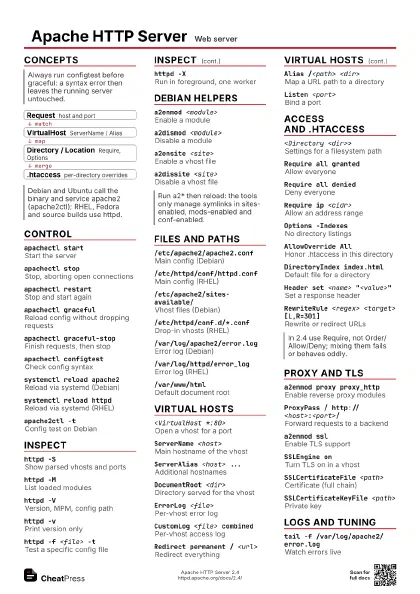
- Request host and port
- VirtualHost ServerName / Alias
- Directory / Location Require, Options
- .htaccess per-directory overrides
Control
apachectl startStart the server
apachectl stopStop, aborting open connections
apachectl restart
Stop and start again
apachectl graceful
Reload config without dropping requests
apachectl graceful-stop
Finish requests, then stop
apachectl configtest
Check config syntax
Prints Syntax OK or the file and line of the error; same as
httpd -t.
apachectl -k <start|stop|graceful>
Pass-through form of the commands
apachectl status
Brief status report
Needs mod_status; fullstatus also needs a text browser such as
lynx.
systemctl reload apache2
Reload via systemd (Debian)
systemctl reload httpd
Reload via systemd (RHEL)
apache2ctl -tConfig test on Debian
Inspect
httpd -SShow parsed vhosts and ports
httpd -MList loaded modules
httpd -VVersion, MPM, config path
httpd -vPrint version only
httpd -lList compiled-in modules
httpd -LList directives of static modules
httpd -t -D DUMP_INCLUDES
Show all included config files
httpd -f <file> -t
Test a specific config file
httpd -XRun in foreground, one worker
httpd -e debug -E <file>
Verbose startup errors to a file
httpd -D <name>
Define a name for <IfDefine>
Debian helpers
a2enmod <module>
Enable a module
a2dismod <module>
Disable a module
a2ensite <site>
Enable a vhost file
a2dissite <site>
Disable a vhost file
a2enconf <conf>
Enable a config snippet
a2query -sList enabled sites
a2query -mList enabled modules
Files and paths
/etc/apache2/apache2.conf
Main config (Debian)
/etc/httpd/conf/httpd.conf
Main config (RHEL)
/etc/apache2/sites-available/
Vhost files (Debian)
/etc/httpd/conf.d/*.conf
Drop-in vhosts (RHEL)
/var/log/apache2/error.log
Error log (Debian)
/var/log/httpd/error_log
Error log (RHEL)
/var/www/htmlDefault document root
Virtual hosts
<VirtualHost *:80>
Open a vhost for a port
ServerName <host>
Main hostname of the vhost
ServerAlias <host> ...
Additional hostnames
DocumentRoot <dir>
Directory served for the vhost
ErrorLog <file>
Per-vhost error log
CustomLog <file> combined
Per-vhost access log
Redirect permanent / <url>
Redirect everything
Alias /<path> <dir>
Map a URL path to a directory
Listen <port>
Bind a port
Include <file>
Include another config file
<IfModule <name>>
Apply only if module is loaded
Access and .htaccess
<Directory <dir>>
Settings for a filesystem path
Require all granted
Allow everyone
Require all denied
Deny everyone
Require ip <cidr>
Allow an address range
Options -Indexes
No directory listings
AllowOverride All
Honor .htaccess in this directory
DirectoryIndex index.html
Default file for a directory
ErrorDocument 404 /<file>
Custom error page
Header set <name> "<value>"
Set a response header
Needs mod_headers.
RewriteRule <regex> <target> [L,R=301]
Rewrite or redirect URLs
Needs mod_rewrite; RewriteEngine On first.
RewriteCond %{HTTPS} off
Condition for the next RewriteRule
AuthType BasicBasic auth, with AuthUserFile
htpasswd -c <file> <user>
Create password file
Drop -c to add users to an existing file.
Proxy and TLS
a2enmod proxy proxy_http
Enable reverse proxy modules
ProxyPass / http://<host>:<port>/
Forward requests to a backend
ProxyPassReverse / http://<host>:<port>/
Rewrite backend redirects
ProxyPreserveHost On
Pass the original Host header
a2enmod sslEnable TLS support
SSLEngine onTurn TLS on in a vhost
SSLCertificateFile <path>
Certificate (full chain)
SSLCertificateKeyFile <path>
Private key
ProxyPass /<path>
                    unix:<sock>|fcgi://localhost/
Hand over to PHP-FPM
Logs and tuning
LogLevel warnSet log verbosity
LogLevel ssl:debug
Raise one module only
tail -f /var/log/apache2/error.log
Watch errors live
ServerTokens Prod
Hide version in headers
KeepAlive OnReuse connections
httpd -V | grep -i mpm
Which MPM is used
MaxRequestWorkers <n>
Cap concurrent requests
a2dismod mpm_prefork && a2enmod mpm_event
Switch MPM (Debian)
Recipes
# test, then reload without dropping requestsapachectl configtest && apachectl gracefulsudo cp <site>.conf /etc/apache2/sites-available/sudo a2ensite <site>sudo apache2ctl configtestsudo systemctl reload apache2<VirtualHost *:80> ServerName <host> ProxyPreserveHost On ProxyPass / http://127.0.0.1:<port>/ ProxyPassReverse / http://127.0.0.1:<port>/</VirtualHost>httpd -Scurl -sI -H "Host: <host>" http://127.0.0.1/