Cheat
OpenLDAP client tools Query LDAP directories
 Light · Postcard
102 × 152 mm · PDF
 Dark · Postcard
102 × 152 mm · PDF
 Ink saver · Postcard
102 × 152 mm · PDF
 Light · A4 landscape
297 × 210 mm · PDF
 Dark · A4 landscape
297 × 210 mm · PDF
 Ink saver · A4 landscape
297 × 210 mm · PDF
 Light · A3 landscape
420 × 297 mm · PDF
 Dark · A3 landscape
420 × 297 mm · PDF
 Ink saver · A3 landscape
420 × 297 mm · PDF
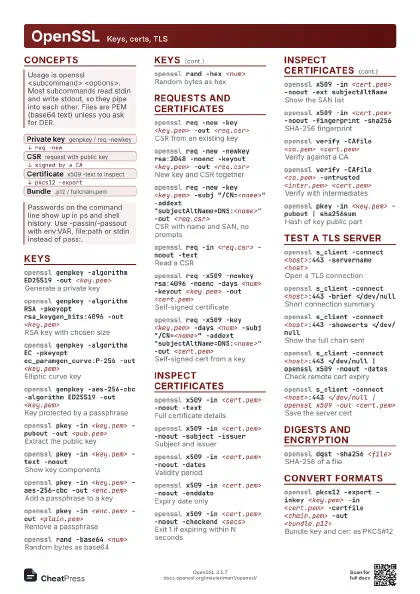
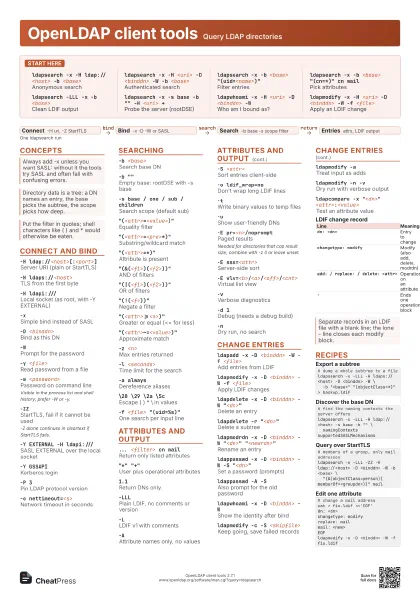
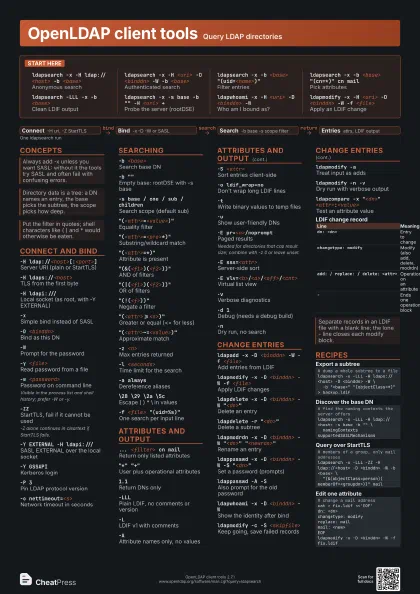
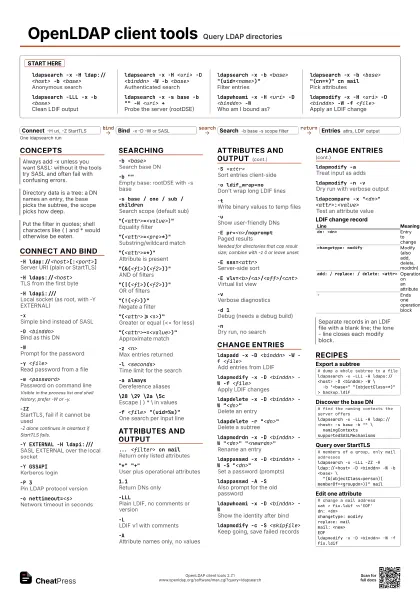
Start here
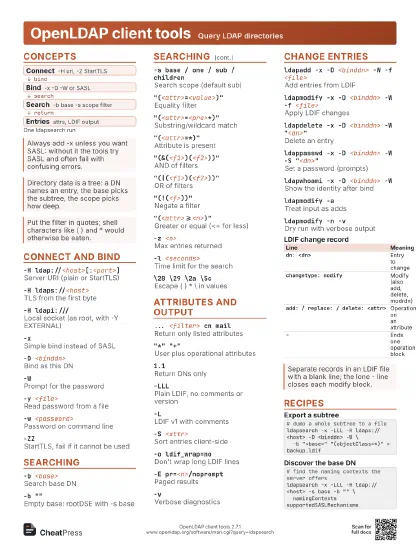
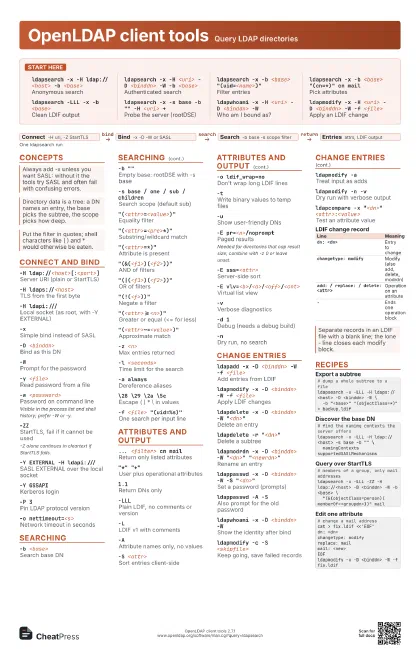
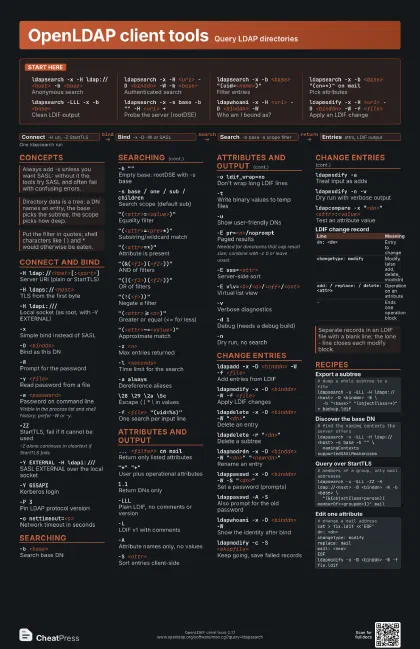
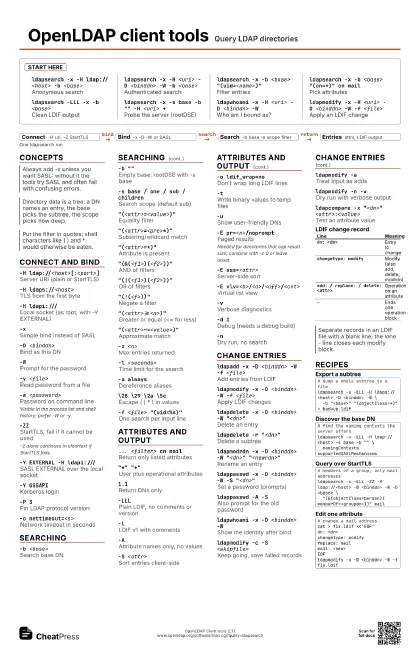
ldapsearch -x -H ldap://<host> -b <base>
Anonymous search
ldapsearch -x -H <uri> -D <binddn> -W -b
                    <base>
Authenticated search
ldapsearch -x -b <base>
                    "(uid=<name>)"
Filter entries
ldapsearch -x -b <base> "(cn=*)" cn
                    mail
Pick attributes
ldapsearch -LLL -x -b <base>
Clean LDIF output
ldapsearch -x -s base -b "" -H <uri>
                    +
Probe the server (rootDSE)
ldapwhoami -x -H <uri> -D <binddn> -W
Who am I bound as?
ldapmodify -x -H <uri> -D <binddn> -W -f
                    <file>
Apply an LDIF change
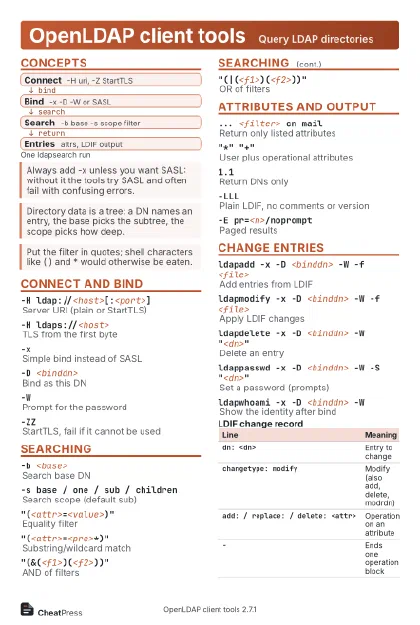
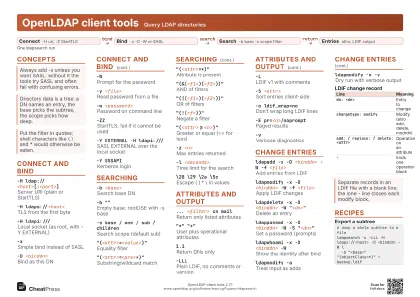
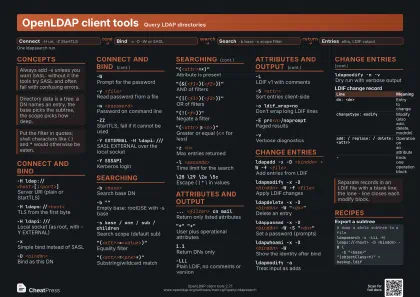
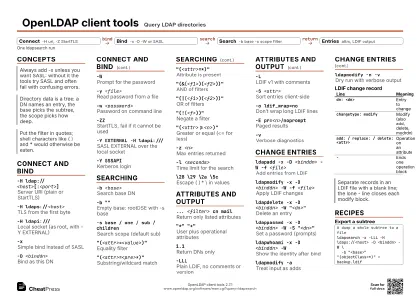
Concepts
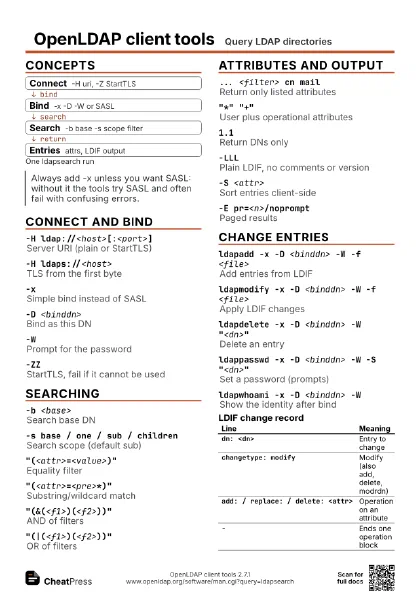
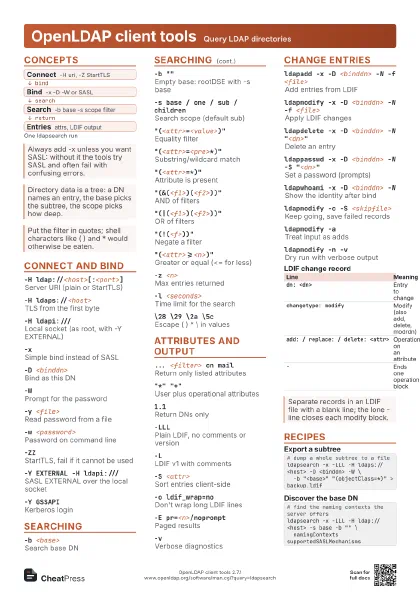
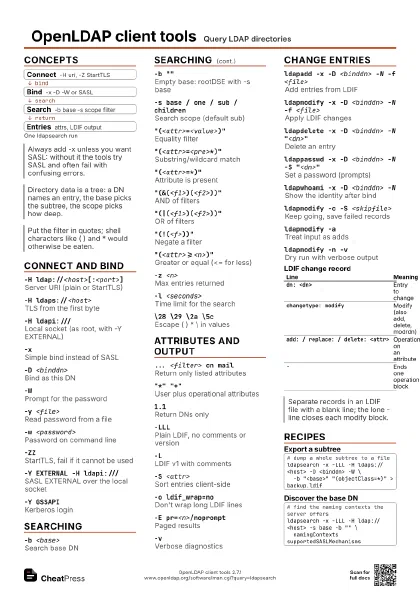
- Connect -H uri, -Z StartTLS
- Bind -x -D -W or SASL
- Search -b base -s scope filter
- Entries attrs, LDIF output
Connect and bind
-H ldap://<host>[:<port>]
Server URI (plain or StartTLS)
-H ldaps://<host>
TLS from the first byte
-H ldapi:///Local socket (as root, with -Y EXTERNAL)
-xSimple bind instead of SASL
-D <binddn>
Bind as this DN
-WPrompt for the password
-y <file>Read password from a file
-w <password>
Password on command line
Visible in the process list and shell history; prefer -W or
-y.
-ZZStartTLS, fail if it cannot be used
-Z alone continues in cleartext if StartTLS fails.
-Y EXTERNAL -H ldapi:///
SASL EXTERNAL over the local socket
-Y GSSAPIKerberos login
-P 3Pin LDAP protocol version
-o nettimeout=<s>
Network timeout in seconds
Searching
-b <base>Search base DN
-b ""Empty base: rootDSE with -s base
-s base / one / sub / children
Search scope (default sub)
"(<attr>=<value>)"
Equality filter
"(<attr>=<pre>*)"
Substring/wildcard match
"(<attr>=*)"
Attribute is present
"(&(<f1>)(<f2>))"
AND of filters
"(|(<f1>)(<f2>))"
OR of filters
"(!(<f>))"
Negate a filter
"(<attr>>=<n>)"
Greater or equal (<= for less)
"(<attr>~=<value>)"
Approximate match
-z <n>Max entries returned
-l <seconds>
Time limit for the search
-a alwaysDereference aliases
\28 \29 \2a \5cEscape ( ) * \ in values
-f <file> "(uid=%s)"
One search per input line
Attributes and output
... <filter> cn mail
Return only listed attributes
"*" "+"
User plus operational attributes
1.1Return DNs only
-LLLPlain LDIF, no comments or version
-LLDIF v1 with comments
-AAttribute names only, no values
-S <attr>Sort entries client-side
-o ldif_wrap=noDon't wrap long LDIF lines
-tWrite binary values to temp files
-uShow user-friendly DNs
-E pr=<n>/noprompt
Paged results
Needed for directories that cap result size; combine with -z 0
or leave unset.
-E sss=<attr>
Server-side sort
-E vlv=<b>/<a>/<off>/<cnt>
Virtual list view
-vVerbose diagnostics
-d 1Debug (needs a debug build)
-nDry run, no search
Change entries
ldapadd -x -D <binddn> -W -f <file>
Add entries from LDIF
ldapmodify -x -D <binddn> -W -f <file>
Apply LDIF changes
ldapdelete -x -D <binddn> -W
                    "<dn>"
Delete an entry
ldapdelete -r "<dn>"
Delete a subtree
ldapmodrdn -x -D <binddn> -W "<dn>"
                    "<newrdn>"
Rename an entry
ldappasswd -x -D <binddn> -W -S
                    "<dn>"
Set a password (prompts)
ldappasswd -A -S
Also prompt for the old password
ldapwhoami -x -D <binddn> -W
Show the identity after bind
ldapmodify -c -S <skipfile>
Keep going, save failed records
ldapmodify -aTreat input as adds
ldapmodify -n -v
Dry run with verbose output
ldapcompare -x "<dn>"
                    <attr>:<value>
Test an attribute value
| Line | Meaning |
|---|---|
dn: <dn> |
Entry to change |
changetype: modify |
Modify (also add, delete, modrdn) |
add: / replace: / delete: <attr>
|
Operation on an attribute |
- |
Ends one operation block |
Recipes
# dump a whole subtree to a fileldapsearch -x -LLL -H ldaps://<host> -D <binddn> -W \ -b "<base>" "(objectClass=*)" > backup.ldif# find the naming contexts the server offersldapsearch -x -LLL -H ldap://<host> -s base -b "" \ namingContexts supportedSASLMechanisms# members of a group, only mail addressesldapsearch -x -LLL -ZZ -H ldap://<host> -D <binddn> -W -b <base> \ "(&(objectClass=person)(memberOf=<groupdn>))" mail# change a mail addresscat > fix.ldif <<'EOF'dn: <dn>changetype: modifyreplace: mailmail: <new>EOFldapmodify -x -D <binddn> -W -f fix.ldif